What is SentinelOne?
SentinelOne is a cybersecurity company whose Singularity Platform combines endpoint protection, endpoint detection and response (EDR), extended detection and response (XDR), cloud workload and cloud-native security, identity security, mobile threat defense and a security data lake with AI-assisted investigation. The company page states that SentinelOne was founded in 2013, is headquartered in Mountain View, California, has been publicly traded on the NYSE under the symbol S since 2021, and reports more than 3,000 employees and more than 18 offices.
The product is sold as a cloud-managed platform: policies, alerts and investigations are handled in a single management console, and a lightweight agent runs on the protected device. According to the platform overview, every customer gets access to the same platform, with a shared data layer, one console and one AI engine, and capabilities are activated as coverage expands. The vendor's materials describe Behavioral AI that runs on the device so protection continues offline, and one-click rollback and remediation for ransomware recovery.
Current modules named on the official site include Singularity Endpoint (with Identity and Mobile), Singularity Cloud, Singularity AI SIEM (which includes Data Pipelines, formerly Observo), Purple AI for natural-language investigation, Hyperautomation for response workflows, the Singularity Marketplace of integrations, Prompt Security, and the Wayfinder managed detection and response and threat hunting services. Packaging is described on the pricing and packages page.
SentinelOne is closed-source commercial software with no self-hosted edition described on its site. Purchases are made through authorized partners, and the vendor lists recognition such as a sixth consecutive year as a Leader in the 2026 Gartner Magic Quadrant for Endpoint Protection Platforms, results in the MITRE ATT&CK Enterprise Evaluation 2024 and a Leader placement in the 2025 IDC MarketScape for Worldwide XDR Software. These are vendor-reported third-party assessments.
Key capabilities
- Singularity Endpoint (EPP and EDR) A single agent provides prevention, detection and response for workstations and servers. The vendor says Behavioral AI blocks ransomware, zero-day exploits, supply chain attacks and fileless malware, and that protection continues when a device is offline. Check supported operating system versions in the customer documentation before a rollout.
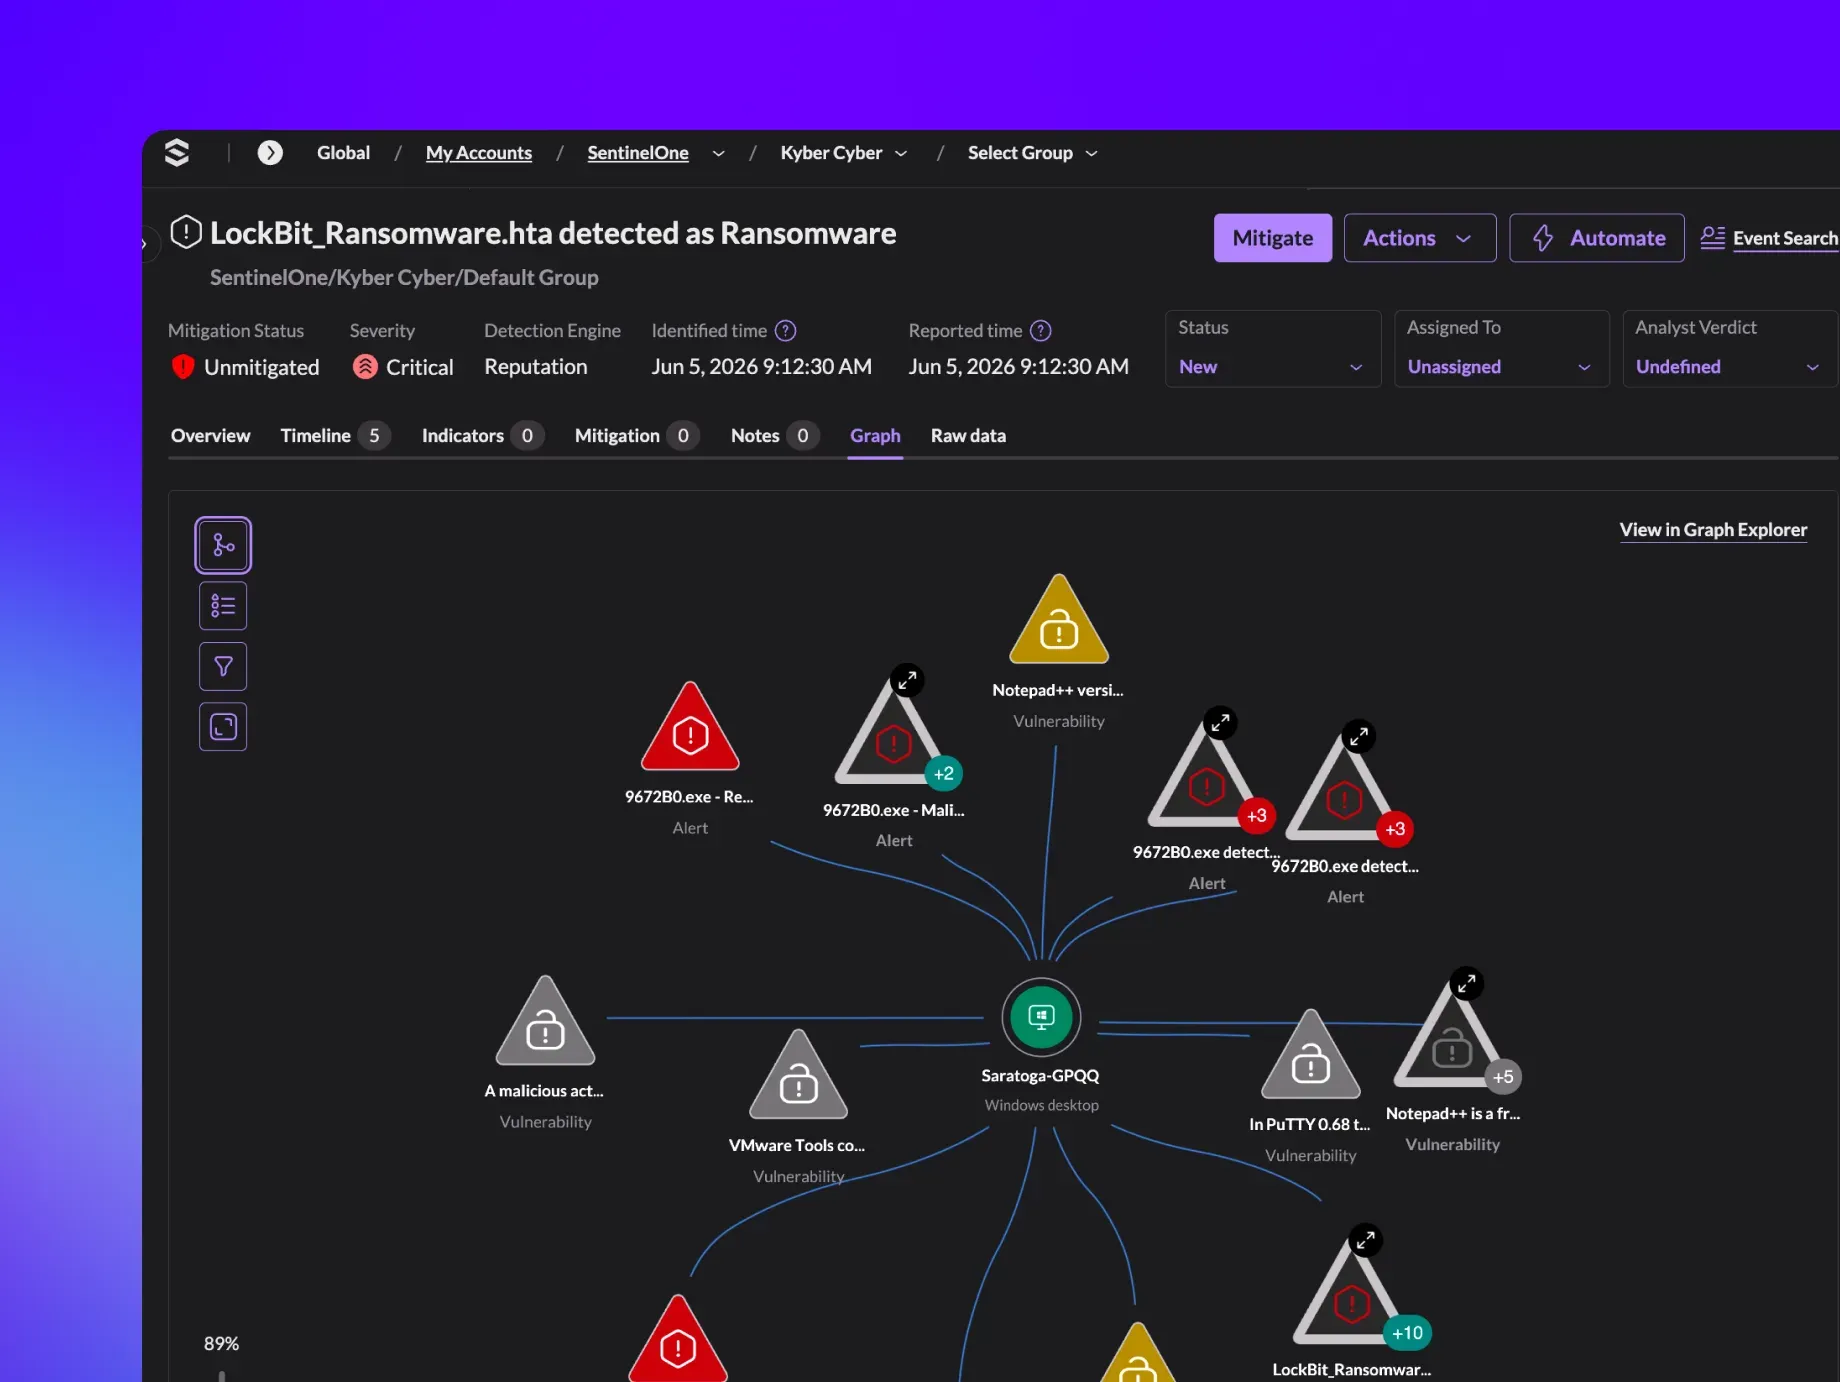
- One-click rollback and remediation The console offers Mitigate actions such as kill, quarantine, remediate, rollback and blocklist, as the official alert screenshot shows. Rollback is marketed as a way to restore systems after ransomware. Test it on a sample machine and confirm what it restores in your environment.
- Singularity Identity Extends the same agent to identity threat detection and response. The vendor lists detection of credential theft, privilege escalation and lateral movement, coverage of Active Directory and identity providers including Entra ID, Okta, Ping, SecureAuth and Duo, and deception and conditional access options. In the packages table it appears from the Commercial tier.
- Singularity Mobile On-device mobile threat defense for iOS, Android and ChromeOS against phishing, malicious apps and network attacks such as rogue Wi-Fi. The official page says it does not require MDM and works without connectivity.
- Singularity Cloud Covers cloud workload security for containers, virtual machines and AI workloads, cloud-native exposure management with verified exploit paths, and cloud data security. The packages page lists a cloud workload protection platform in the Singularity Complete tier.
- Singularity AI SIEM A security data platform that ingests cloud, identity, endpoint and third-party data, normalizes it and supports hunting and investigation. Singularity Data Pipelines, formerly Observo, handle normalization, enrichment and routing before data reaches storage.
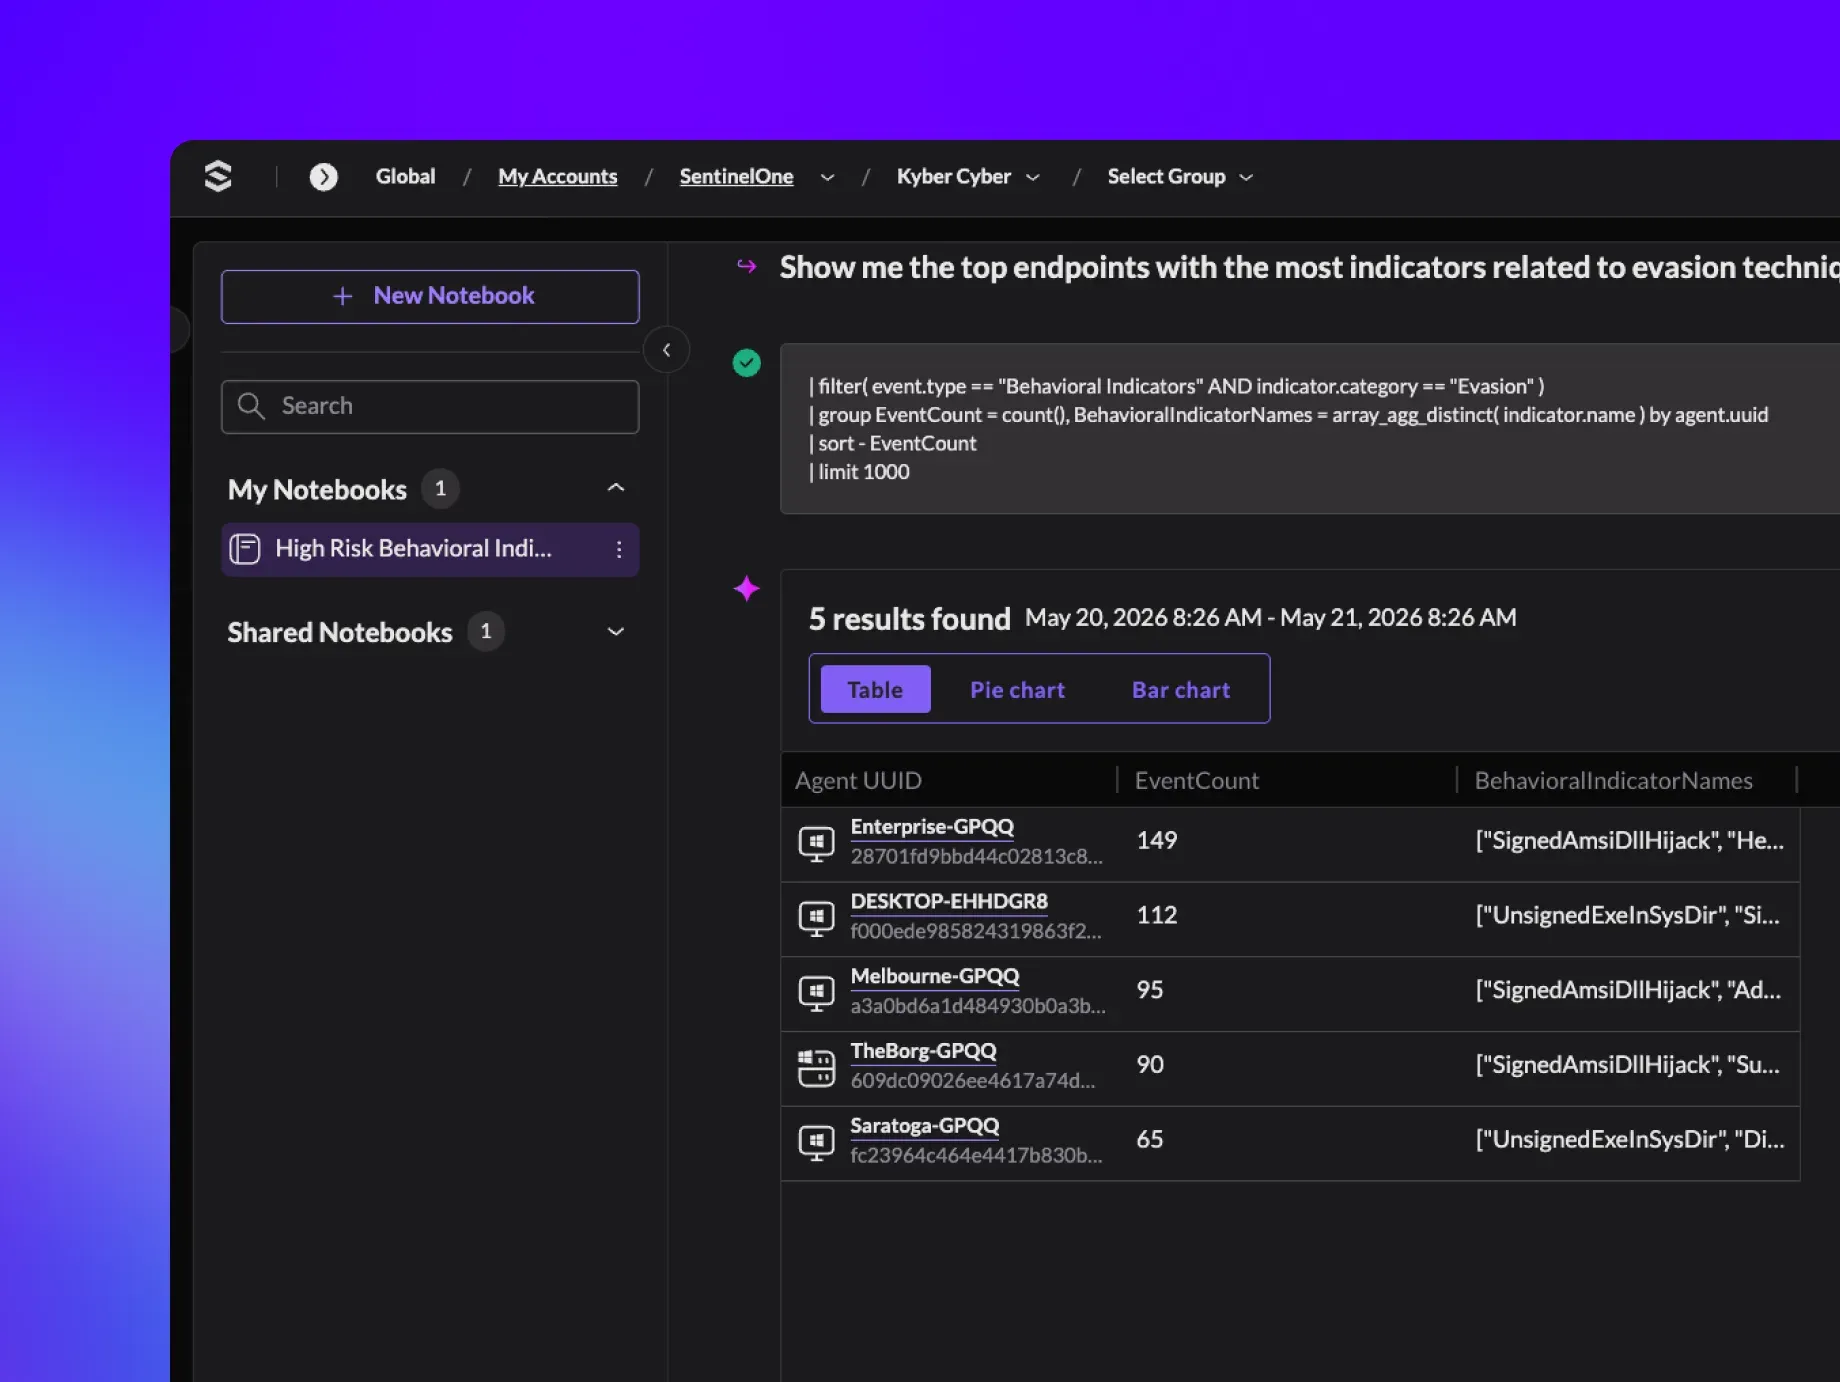
- Purple AI An AI security analyst that turns questions into queries and summarizes findings. The official screenshot shows a notebook that translates a natural-language request about evasion techniques into a query and a results table. The packages page lists an AI Security Assistant from Complete and an agentic AI SOC analyst for automated triage in Enterprise.
- Hyperautomation Workflow automation for containment and remediation, started from the investigation console. The vendor states it connects to common SaaS tools and any system with an API. Keep an approval step for destructive actions.
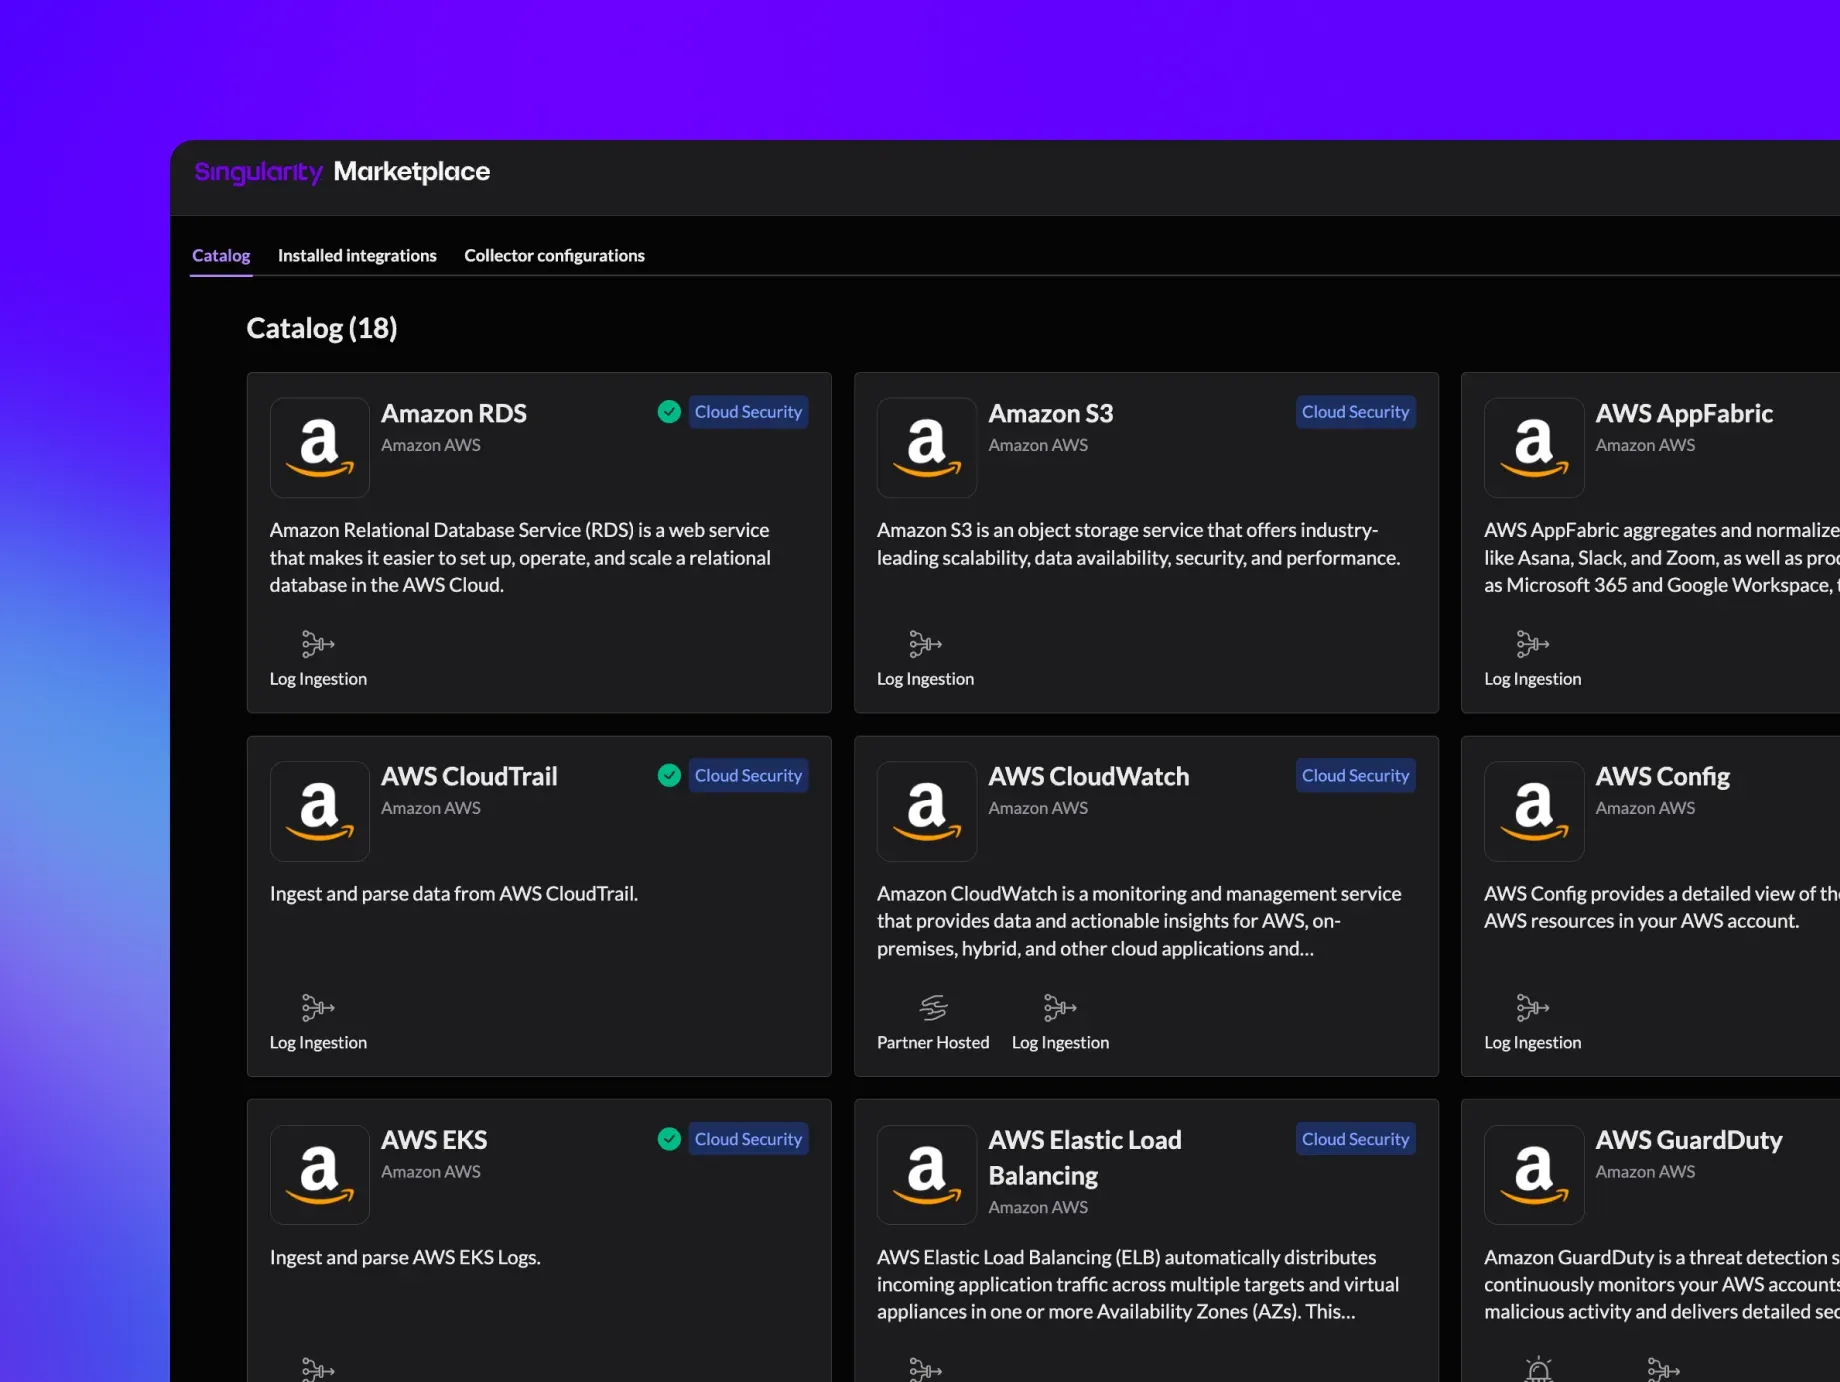
- Singularity Marketplace A catalog of integrations with collectors for log ingestion and response actions, including AWS sources such as CloudTrail, S3 and GuardDuty in the official screenshot. Each integration page states its direction, such as log ingestion or partner-hosted.
- Attack graph in alert detail The console shows a graph linking alerts, vulnerabilities and the affected host for an incident, so an analyst sees related alerts together rather than one by one. Alert detail tabs include timeline, indicators, mitigation, notes, graph and raw data.
- Network discovery and forensics The Enterprise package lists network discovery and forensic data collection for deeper investigation. Plan storage and retention with your incident response team, since longer collection increases data volume.
- Data retention tiers The packages page lists 14 days of data retention for Singularity Complete and 90 days for Commercial. Retention affects how far back threat hunting can reach, so compare it with your investigation and compliance needs.
- Wayfinder MDR and managed services Wayfinder Threat Detection and Response offers 24/7 monitoring, investigation and response by SentinelOne analysts, alongside threat hunting and incident readiness and response services. Managed threat hunting is listed from the Commercial tier, while Wayfinder MDR is described as a separate service.
- Multi-tenant management and access control All packages list role-based access control and multi-tenant management, which matters for MSSPs and organizations with several business units. The company runs a partner program and an MSSP offering.
- Federal and industry options The site says SentinelOne is FedRAMP High authorized for federal government customers, and publishes industry pages for healthcare, financial services, manufacturing, education and others. Confirm the authorization scope for your agency or workload directly with the vendor.
- Pricing (published list prices) Singularity Complete is listed at $179.99 per endpoint per year, Commercial at $229.99, and Enterprise on request. The page states prices apply to 5 to 100 workstations, exclude taxes and are final only through an authorized partner.
Where SentinelOne fits
Replacing legacy antivirus with EDR
Start with a pilot group of managed devices, run the agent in detect-only mode if your policy allows, and review the alerts before enabling protect mode. Check exclusions for line-of-business software and confirm the removal of the previous security agent. The Complete tier covers endpoint and cloud workload protection with 14 days of retention.
Responding to ransomware
Use the alert graph to see which processes and hosts are involved, then apply mitigation, quarantine or rollback from the console. Rehearse the sequence on a test host so responders know which actions are reversible and who approves them. Keep offline backups regardless of rollback features, and record who may approve a rollback so the decision is not made during the incident.
Extending to identity and cloud
Add Identity detection for Active Directory and cloud identity providers, and cloud workload protection for servers and containers. Map each module to an asset inventory so that coverage gaps are visible, and confirm which tier includes the modules you need before purchase.
Building a SOC on the data platform
Ingest endpoint, identity, cloud and third-party sources through the Marketplace and Data Pipelines, then use Purple AI for investigation and Hyperautomation for response. Measure false positives and time to triage during a trial against your own alert history, and decide which automated actions need human approval. The vendor's published time savings are its own figures.
Running as a managed service provider
Multi-tenant management and role-based access control support separate customer accounts. Review billing through the partner program, per-tenant policies and data separation, and consider adding Wayfinder MDR where 24/7 coverage is required. Agree on reporting, escalation paths and a clear offboarding process for each customer tenant.
Reviews of SentinelOne
Be the first to share your experience with SentinelOne.
Write a review
Loading review form…
Found SentinelOne useful? Upvote it todayYour vote helps other IT teams find it in the daily ranking.