

What is Elastic Security?
Elastic Security is the security solution of Elastic, built into Kibana and storing its data in Elasticsearch. Elastic's product page calls it an "open, agentic security operations platform" that combines SIEM, endpoint security (EDR), XDR and automated response, and the documentation describes it as a way to detect, investigate and respond to threats across hosts, cloud services and networks. According to the requirements page, it needs an Elasticsearch cluster with Kibana, at least one node with the transform role, and third-party data mapped to the Elastic Common Schema (ECS).
The SIEM side runs a detection engine with prebuilt rules, custom rules and machine learning jobs, with alerts triaged in the Alerts page, Timeline and cases. Elastic Defend, an Elastic Agent integration, prevents malware, ransomware and in-memory threats on Windows, macOS and Linux and adds response actions such as host isolation. Cloud security covers posture management (CSPM, KSPM) and vulnerability scanning of AWS Linux virtual machines (CNVM). AI features include the AI Assistant, Attack Discovery and Automatic Migration of rules from Splunk, QRadar and Microsoft Sentinel.
Detection content is developed in public. The elastic/detection-rules repository is "the home for rules used by Elastic Security", and Elastic's product page counts more than 1,900 open detection rules on GitHub. Endpoint behavior rules and YARA signatures used by Elastic Defend are published in elastic/protections-artifacts. Both repositories use the Elastic License 2.0 (ELv2), and the Security application code sits in the ELv2-only x-pack folder of the Kibana repository.
Elastic Security ships with each Elastic Stack release. The current stack release is 9.5.6, published on GitHub on November 2, 2026. The Elastic Security 9.5.6 release notes list faster bulk updates when importing rules with overwrite, CPU utilization limits from 1 to 100 percent for Elastic Defend, a default malware scan file size limit of 150 MiB and more reliable macOS system extension management. Version 9.5.0 made detection rule change history generally available with restore of earlier rule states, installed prebuilt rules about five times faster and updated MITRE ATT&CK mappings to v19.1. Serverless Security projects on Elastic Cloud are updated continuously and have no version to choose.
Elastic Security runs self-managed, on Elastic Cloud Hosted or as a Serverless Security project. On self-managed clusters, the free Basic subscription includes the SIEM, detection engine, prebuilt rules, cases and malware prevention; Platinum adds machine learning detections, ransomware protection and host isolation; Enterprise adds the AI Assistant, Attack Discovery and the response console. Self-managed prices are not published. On November 20, 2026, the Serverless Security pricing page listed Security Analytics Essentials from $0.09 per GB ingested and Complete from $0.11 per GB, with endpoint protection included without per-endpoint fees since March 23, 2026. Comparable products on iThub include Splunk, SentinelOne and CrowdStrike; the underlying engine is listed as Elasticsearch.
Key capabilities
- Detection engine Rules run on a schedule against Elasticsearch indices and create alerts. The rule types are custom query (KQL or Lucene), event correlation (EQL), ES|QL, threshold, indicator match against threat intelligence indices, new terms for values not seen in a history window, and machine learning anomaly rules. The detection engine and prebuilt rules are part of the free Basic tier.
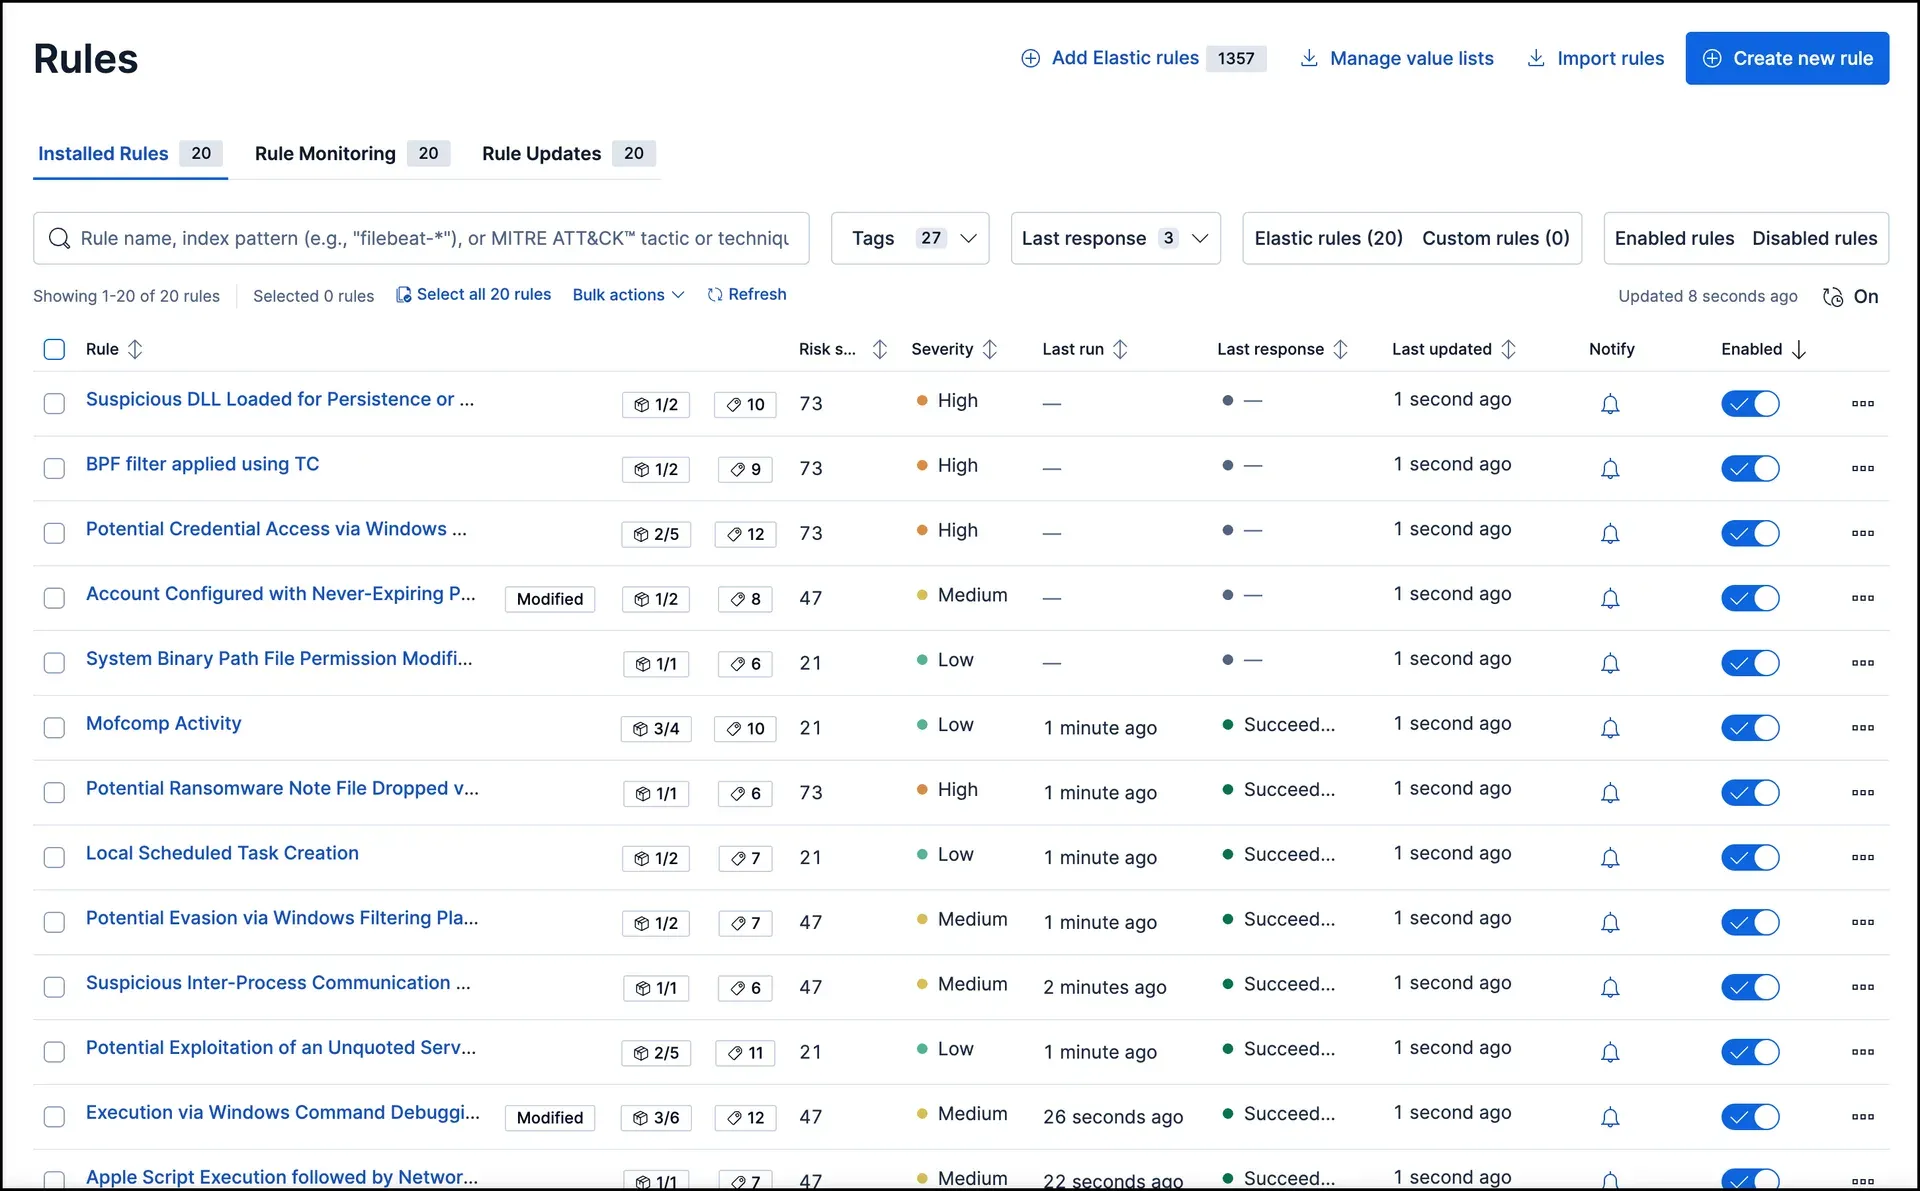
- Prebuilt detection rules Elastic maintains prebuilt rules tagged by MITRE ATT&CK tactic, installed from the Detection rules (SIEM) page and not enabled by default. On all tiers, rules can be duplicated and customized, given exceptions and actions, and updated from Elastic. Editing prebuilt rules directly and resolving update conflicts require Enterprise or Serverless Complete, according to the prebuilt rules guide.
- Detections as code The detection-rules repository stores rules as TOML files and ships a Python 3.12+ module for parsing, validating and packaging them, a KQL parser, a library for the Kibana detection API, building block rules and a hunting query library. Teams use it to manage custom rules in Git and push them to Kibana.
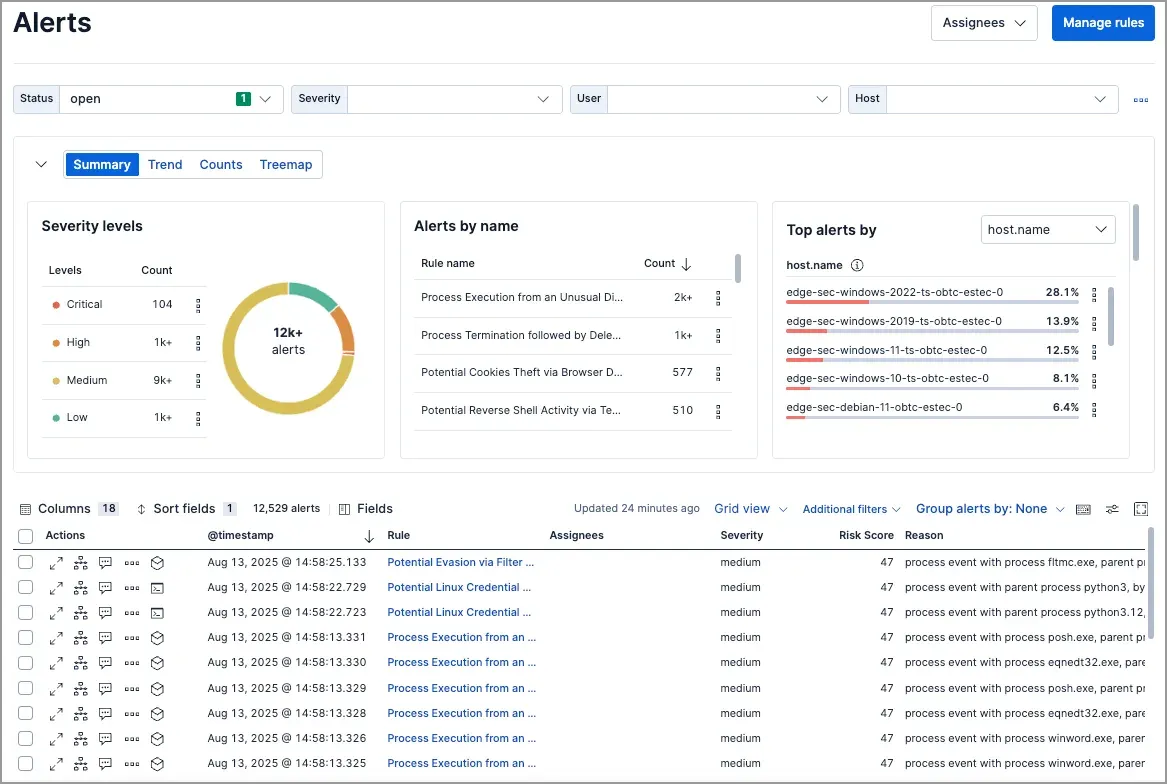
- Alerts triage The Alerts page summarizes alerts by severity, rule and host, and lists each alert with risk score, rule, assignee and reason. Alerts can be grouped, filtered, assigned and acknowledged, and opened in Timeline or the event analyzer, as described in the alert management guide. Alert suppression and Analyst Insights are Platinum features.
- Timeline and visual event analyzer Timeline is an investigation workspace for querying events with KQL, EQL correlation or ES|QL, pinning events and adding notes. The visual event analyzer draws a process tree for an alert and shows related network, file and registry events for each process.
- Cases Cases collect alerts, comments, observables and files for an investigation, with custom fields and templates. Case management is in Basic; user assignment is Platinum, and connectors that push cases to Jira, ServiceNow, IBM Resilient or Swimlane follow the tiers on the subscription matrix.
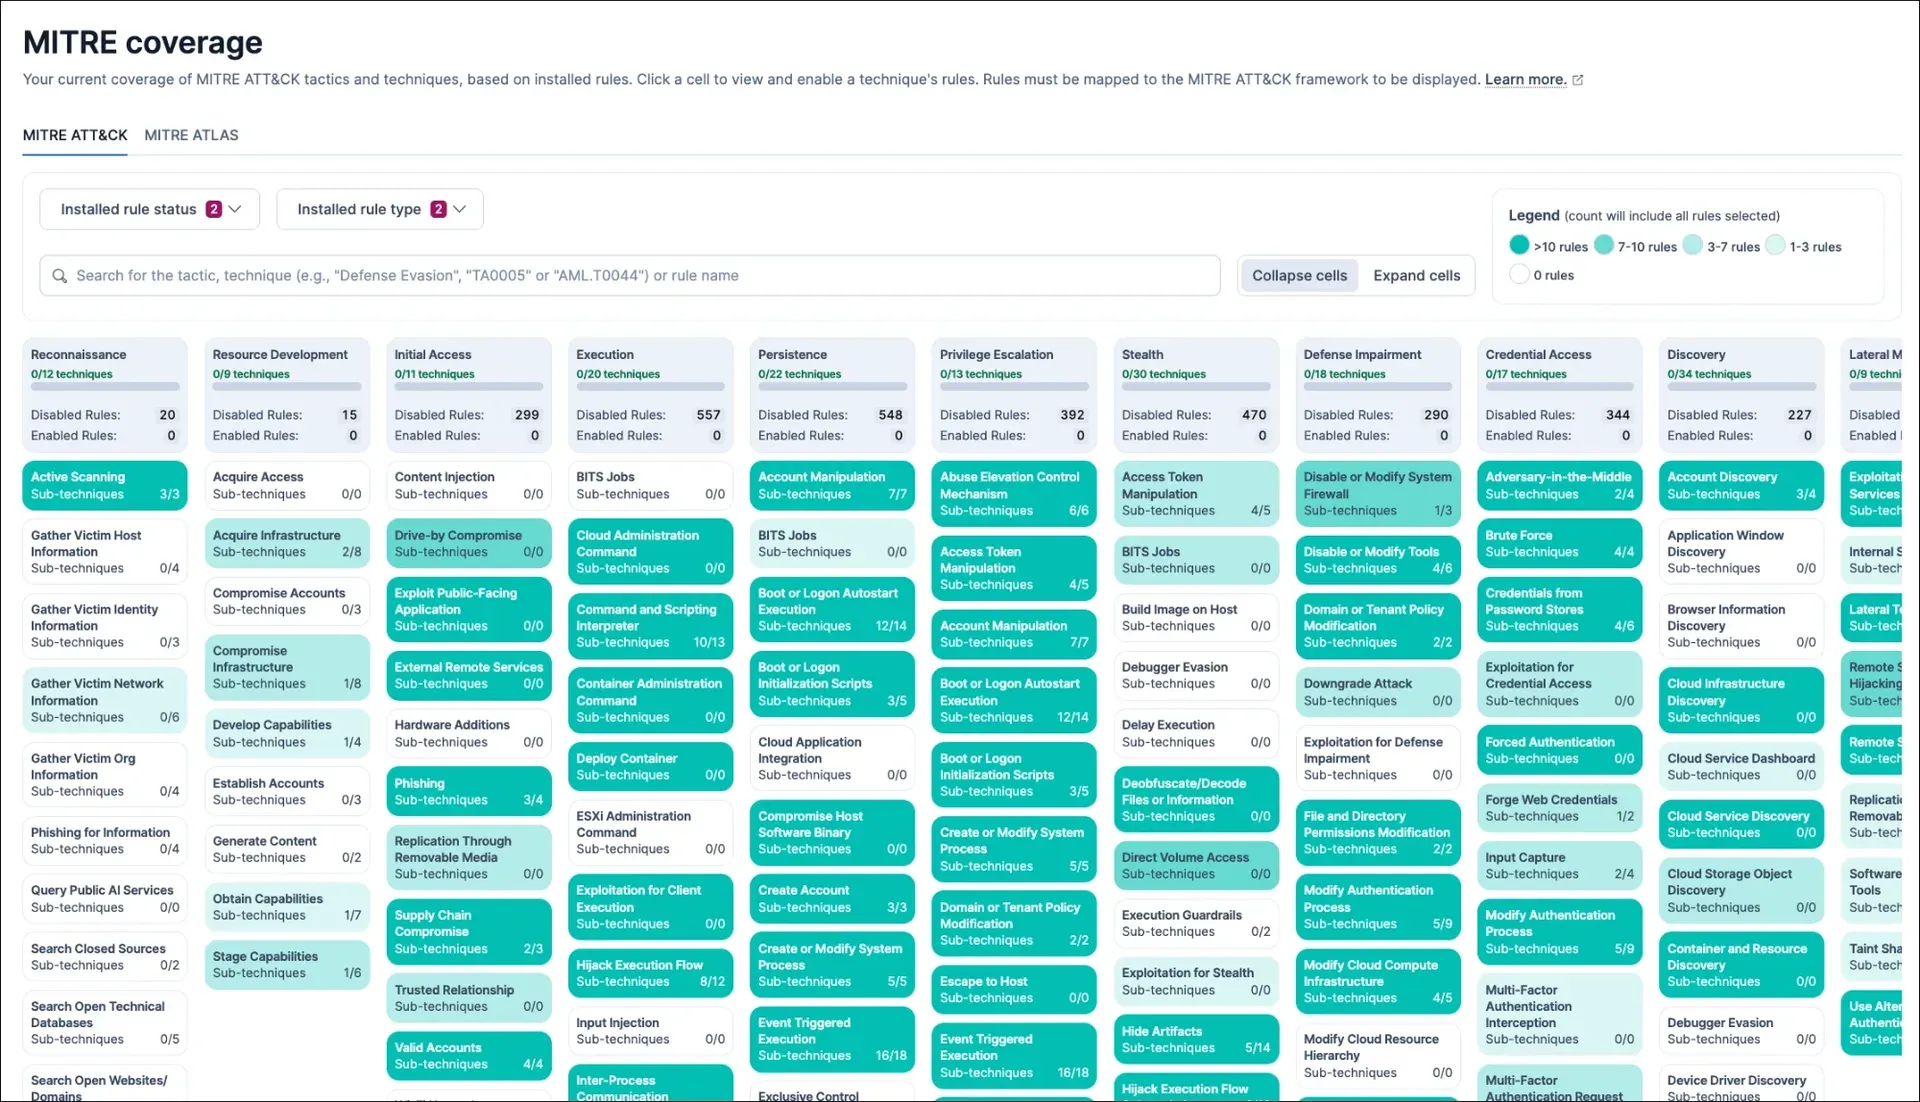
- MITRE ATT&CK coverage A coverage page maps installed rules to ATT&CK tactics, techniques and sub-techniques, with filters for enabled, disabled, Elastic and custom rules. A second tab shows coverage of MITRE ATLAS techniques for AI systems.
- Elastic Defend Elastic Defend is added to Elastic Agent policies through Fleet with presets for traditional endpoints (Data Collection, Next-Generation Antivirus, Essential EDR, Complete EDR) and for cloud workloads on Linux. It requires Fleet, cannot run with Elastic Agent in standalone mode or in a Kubernetes DaemonSet, and the requirements page lists under 2 percent CPU, 1 GB of disk and 500 MB of RSS memory.
- Endpoint protection by tier Malware prevention and admin-defined blocklists are in Basic, tamper protection starts at the paid tiers, ransomware prevention, malicious behavior protection, memory threat protection, self healing and host isolation are Platinum, and Device Control is Enterprise. Behavior rules, YARA signatures and the ransomware artifact are published in protections-artifacts.
- Response actions The response console sends commands to Elastic Defend hosts:
isolate,release,status,processes,kill-process,suspend-process,get-file,upload,scan,execute,runscriptandmemory-dump. Selected actions also work on hosts protected by CrowdStrike, SentinelOne or Microsoft Defender for Endpoint. The interactive response console is an Enterprise feature. - Osquery The Osquery Manager integration runs live SQL queries and scheduled packs against hosts with Elastic Agent and attaches results to alerts and cases. Version 9.5 added Daily and Custom recurring schedules for packs and export of results as CSV, JSON or NDJSON, according to the Osquery documentation.
- Entity analytics Entity analytics assigns hosts, users and services a risk score from 0 to 100 based on alerts and asset criticality, and the entity store combines log, identity provider and risk data into one view per entity. Risk scoring and watchlists are Platinum; entity resolution and AI skills are Enterprise.
- Cloud security CSPM and KSPM check cloud accounts and Kubernetes clusters against security benchmarks, CNVM scans Linux virtual machines on AWS for known vulnerabilities, and Elastic Defend for Containers alerts on drift in Kubernetes containers (beta). On self-managed subscriptions, CSPM and KSPM are Enterprise features.
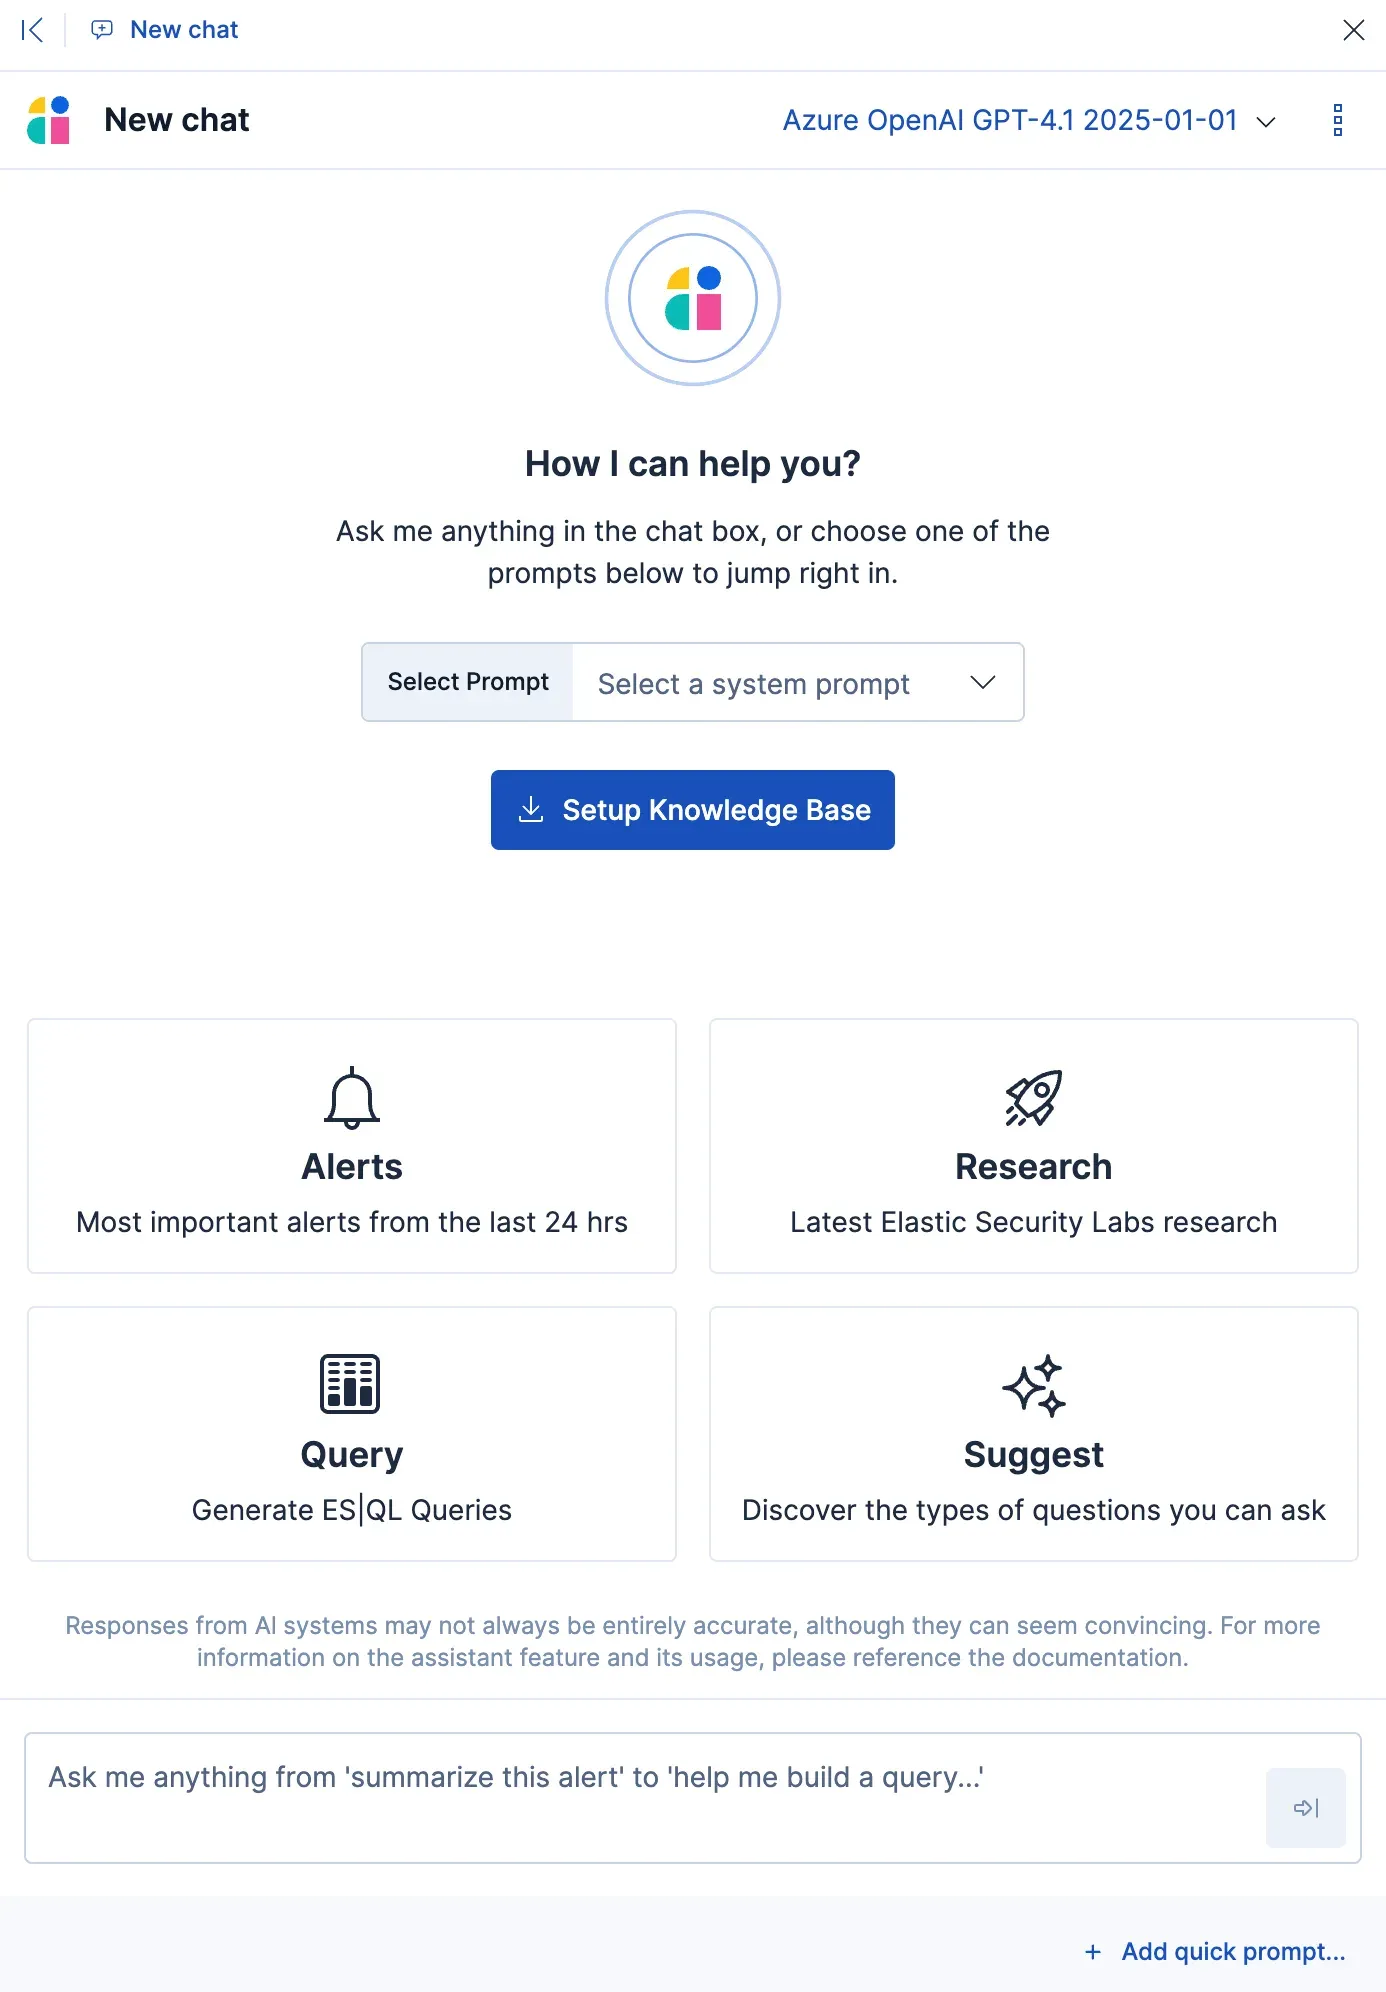
- Elastic AI Assistant The AI Assistant is a chat interface for alert investigation, incident response and ES|QL query generation. It needs an Enterprise subscription or the Serverless Complete or EASE tier, a machine learning node and an LLM connector such as OpenAI, Azure OpenAI, Amazon Bedrock or the Elastic Managed LLM. An anonymization setting controls which fields are sent to the model, and a knowledge base stores context. Since 9.4, Elastic Agent Builder is the default chat experience, and AI Assistant can be selected in GenAI Settings.
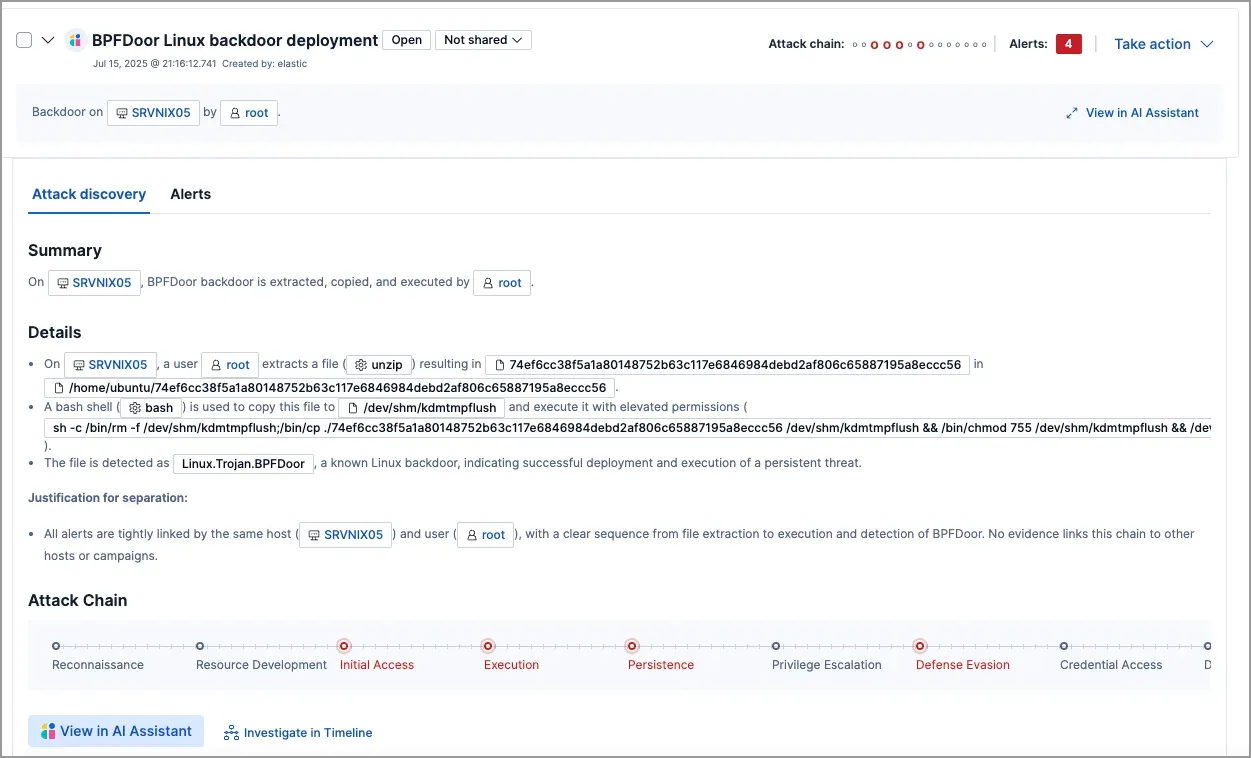
- Attack Discovery Attack Discovery sends alerts to an LLM and returns discoveries that group related alerts into one attack, with the hosts and users involved, an ATT&CK attack chain and links to Timeline and the AI Assistant. Runs can be started manually, on a schedule, from a workflow or from an Agent Builder conversation. It is an Enterprise feature on self-managed subscriptions.
- Automatic Migration Automatic Migration uses an LLM to translate Splunk rules and dashboards, QRadar rules and, in preview since 9.5, Microsoft Sentinel rules into Elastic Security rules and dashboards for review. It requires Enterprise with machine learning on Elastic Stack, or Security Complete on Serverless.
- Data ingestion Data arrives through Elastic Agent integrations, Beats, Logstash or third-party sources, and has to follow ECS. Third-party OpenTelemetry collectors that do not map data to ECS are not supported. The ingest guide describes the supported paths, and Elastic's product page lists more than 400 integrations.
- Detection and response APIs Detection rules and alerts can be managed through the Kibana Security detections API, which the detection-rules tooling also uses.
Where Elastic Security fits
Running a SIEM on existing log data
A security team adds integrations for its cloud accounts, identity provider, firewalls and servers to Elastic Agent policies, so events land in ECS-mapped data streams. Prebuilt rules matching those data sources are installed and enabled from the Rules page, and the MITRE ATT&CK coverage page shows which tactics the enabled rules cover. Alerts then appear on the Alerts page with severity and risk score.
Endpoint protection and EDR
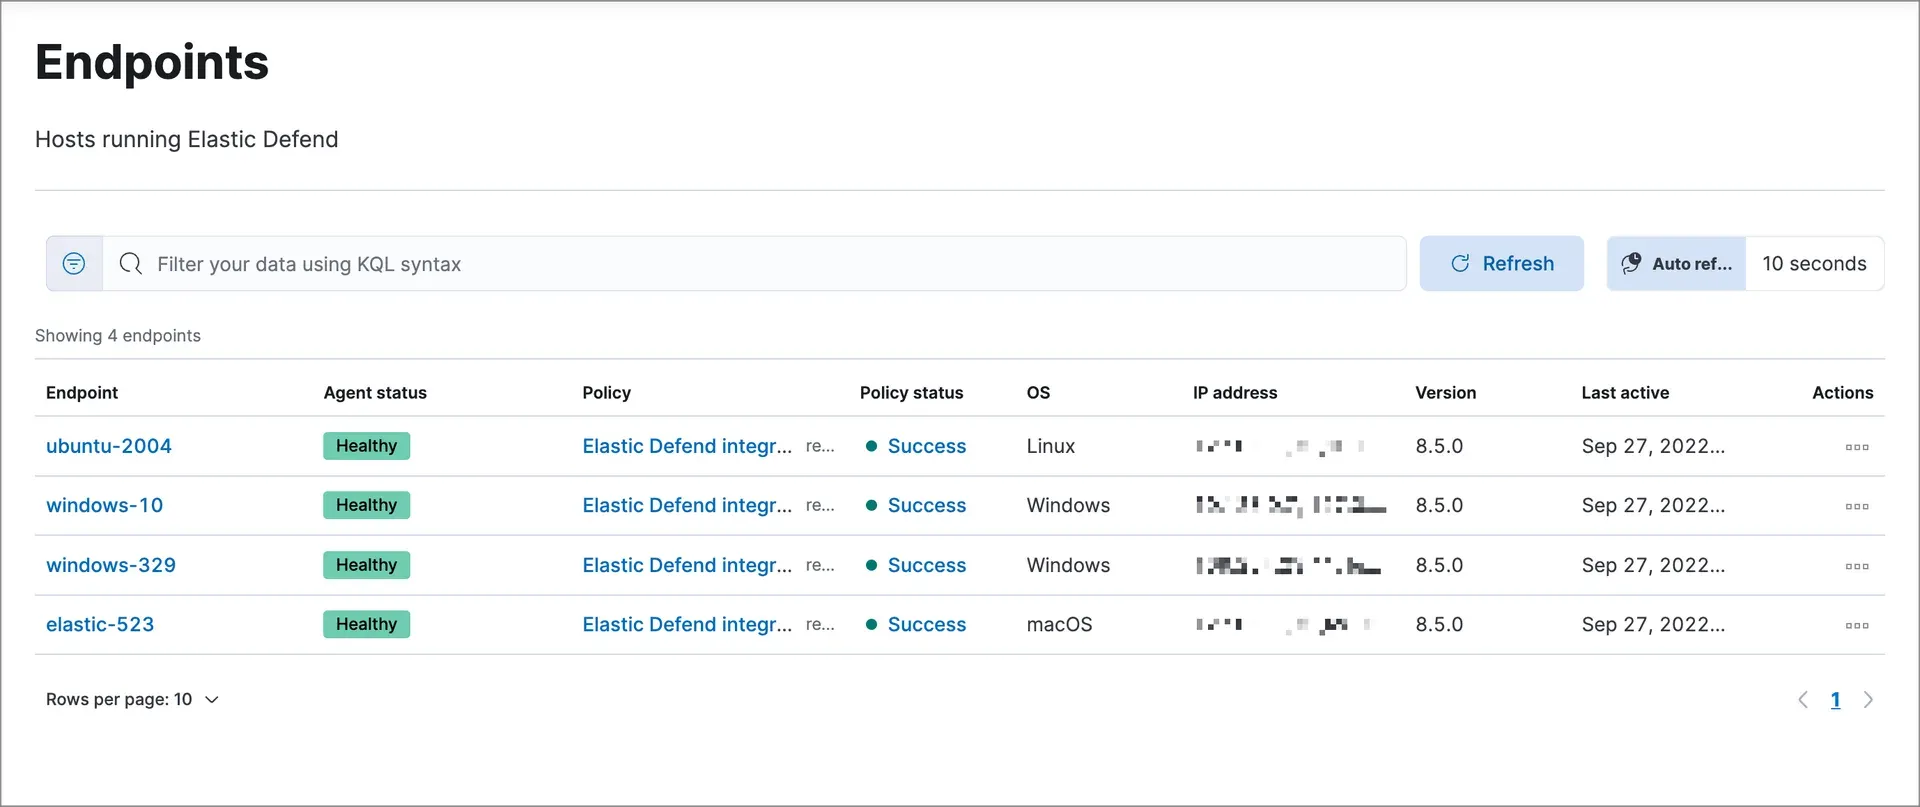
Elastic Defend is added to an agent policy with one of the presets, for example Complete EDR, and agents enrolled through Fleet on Windows, macOS and Linux hosts start sending process, network and file events. Prevention settings for malware, ransomware, behavior and memory threats follow the subscription tier, and the Endpoints page lists each host with its policy status. Response actions such as isolating a host or retrieving a file are run from the response console.
Triage and investigation
An analyst filters open alerts, groups them by rule or host and opens an alert in Timeline or the visual event analyzer to follow the process tree. Attack Discovery can group related alerts into attack narratives mapped to ATT&CK, and the AI Assistant or Agent Builder can summarize alerts or draft ES|QL queries. Findings, alerts and observables are collected in a case.
Detection engineering as code
Detection engineers keep custom rules in a Git repository based on the detection-rules tooling, validate them with its Python module and unit tests, and deploy them to Kibana through the detection API. Elastic develops its prebuilt rules in the same public repository.
Migrating from another SIEM
Teams moving from Splunk, QRadar or Microsoft Sentinel export their rules (and, for Splunk, dashboards) and upload them to Automatic Migration, which uses the configured LLM connector to translate them into Elastic Security rules and dashboards. The translated rules are reviewed and edited before they are installed and enabled like other custom rules.
Cloud and Kubernetes posture
CSPM and KSPM integrations evaluate cloud accounts and Kubernetes clusters against CIS benchmarks and report deviations as findings, while CNVM scans AWS Linux virtual machines for known vulnerabilities. On Serverless, these run as the Cloud Protection add-on priced per billable asset, as listed on the Serverless Security pricing page.
Reviews of Elastic Security
Be the first to share your experience with Elastic Security.
Write a review
Loading review form…
Found Elastic Security useful? Upvote it todayYour vote helps other IT teams find it in the daily ranking.


