
What is Vooki Pro DAST?
Vooki Pro - Desktop DAST Solution for Web Applications and REST APIs
Vooki Pro is a cross-platform desktop Dynamic Application Security Testing (DAST) solution for identifying, analyzing, and retesting security vulnerabilities in web applications and REST APIs. It supports Windows, macOS, and Linux.
Vooki Pro performs security testing locally on the user's machine. Scan results, findings, and HTTP request/response evidence are stored in a local SQLite database. Its AI-powered analysis engine, ThreatLens, runs on-device to assist with vulnerability analysis and triage.
Key Features
1. Application Discovery
Quick seed-based discovery
Automated crawling
Browser recording
Hybrid discovery combining multiple methods
Configurable crawl depth, URL limits, and time budgets
2. Web and REST API Security Scanning
Dynamic security testing using built-in and custom policies
OpenAPI v2/v3 specification imports
Postman collection imports
HAR file imports
Coverage for common web application and API vulnerabilities
3. Authentication Testing
Form-based login
Token-based authentication
OAuth 2.0 authentication
Recorded browser sessions
Automatic token refresh
Session-expiry detection
4. Vulnerability Analysis and Retesting
Detailed HTTP request and response evidence
On-device AI-powered vulnerability triage using Threat Lens
Retesting with the original vulnerability detector
Finding statuses: Fixed, Still Vulnerable, and Needs Review
5. Automation and CI/CD Integration
Scheduled scans using cron or interval-based scheduling
Headless command-line interface (CLI)
CI/CD build failure based on configurable vulnerability severity thresholds
6. Vulnerability Coverage
Vooki Pro detects and assesses vulnerabilities including:
SQL Injection and other injection vulnerabilities
Cross-Site Scripting (XSS)
Broken Access Control
Authentication and JWT security issues
Server-Side Request Forgery (SSRF)
API vulnerabilities, including BOLA, BFLA, BOPLA, and Mass Assignment
Security header misconfigurations
Cookie security issues
Cross-Site Request Forgery (CSRF)
Outdated component detection
API security findings are mapped to the OWASP API Security Top 10.
7. Reporting and Compliance
Export reports in PDF, HTML, DOCX, and JSON formats
CLI report generation in JSON,PDF, DOCX, and HTML formats
Compliance reports mapped to seven security frameworks
8. Issue Tracking and Notifications
Jira
GitHub
Linear
GitLab
Azure DevOps
Slack notifications
Webhook alerts
Deployment and Data Privacy
Vooki Pro is a desktop application that runs locally on Windows, macOS, and Linux. Scan data, findings, and HTTP evidence are stored in a local SQLite database on the user's machine. The AI analysis model runs on-device.
Licensing and Trial
Annual licensing
Per-domain licensing, including subdomains
7-day full-feature free trial
Scope and Limitations
Vooki Pro focuses on dynamic security testing of web applications and REST APIs. It does not provide:
Static Application Security Testing (SAST)
Software Composition Analysis (SCA)
Network scanning
Mobile APK scanning
Manual penetration testing tools such as proxy, repeater, or fuzzer.
Vooki Pro is a cross-platform desktop Dynamic Application Security Testing (DAST) solution for identifying, analyzing, and retesting security vulnerabilities in web applications and REST APIs. It supports Windows, macOS, and Linux.
Vooki Pro performs security testing locally on the user's machine. Scan results, findings, and HTTP request/response evidence are stored in a local SQLite database. Its AI-powered analysis engine, ThreatLens, runs on-device to assist with vulnerability analysis and triage.
Key Features
1. Application Discovery
Quick seed-based discovery
Automated crawling
Browser recording
Hybrid discovery combining multiple methods
Configurable crawl depth, URL limits, and time budgets
2. Web and REST API Security Scanning
Dynamic security testing using built-in and custom policies
OpenAPI v2/v3 specification imports
Postman collection imports
HAR file imports
Coverage for common web application and API vulnerabilities
3. Authentication Testing
Form-based login
Token-based authentication
OAuth 2.0 authentication
Recorded browser sessions
Automatic token refresh
Session-expiry detection
4. Vulnerability Analysis and Retesting
Detailed HTTP request and response evidence
On-device AI-powered vulnerability triage using Threat Lens
Retesting with the original vulnerability detector
Finding statuses: Fixed, Still Vulnerable, and Needs Review
5. Automation and CI/CD Integration
Scheduled scans using cron or interval-based scheduling
Headless command-line interface (CLI)
CI/CD build failure based on configurable vulnerability severity thresholds
6. Vulnerability Coverage
Vooki Pro detects and assesses vulnerabilities including:
SQL Injection and other injection vulnerabilities
Cross-Site Scripting (XSS)
Broken Access Control
Authentication and JWT security issues
Server-Side Request Forgery (SSRF)
API vulnerabilities, including BOLA, BFLA, BOPLA, and Mass Assignment
Security header misconfigurations
Cookie security issues
Cross-Site Request Forgery (CSRF)
Outdated component detection
API security findings are mapped to the OWASP API Security Top 10.
7. Reporting and Compliance
Export reports in PDF, HTML, DOCX, and JSON formats
CLI report generation in JSON,PDF, DOCX, and HTML formats
Compliance reports mapped to seven security frameworks
8. Issue Tracking and Notifications
Jira
GitHub
Linear
GitLab
Azure DevOps
Slack notifications
Webhook alerts
Deployment and Data Privacy
Vooki Pro is a desktop application that runs locally on Windows, macOS, and Linux. Scan data, findings, and HTTP evidence are stored in a local SQLite database on the user's machine. The AI analysis model runs on-device.
Licensing and Trial
Annual licensing
Per-domain licensing, including subdomains
7-day full-feature free trial
Scope and Limitations
Vooki Pro focuses on dynamic security testing of web applications and REST APIs. It does not provide:
Static Application Security Testing (SAST)
Software Composition Analysis (SCA)
Network scanning
Mobile APK scanning
Manual penetration testing tools such as proxy, repeater, or fuzzer.
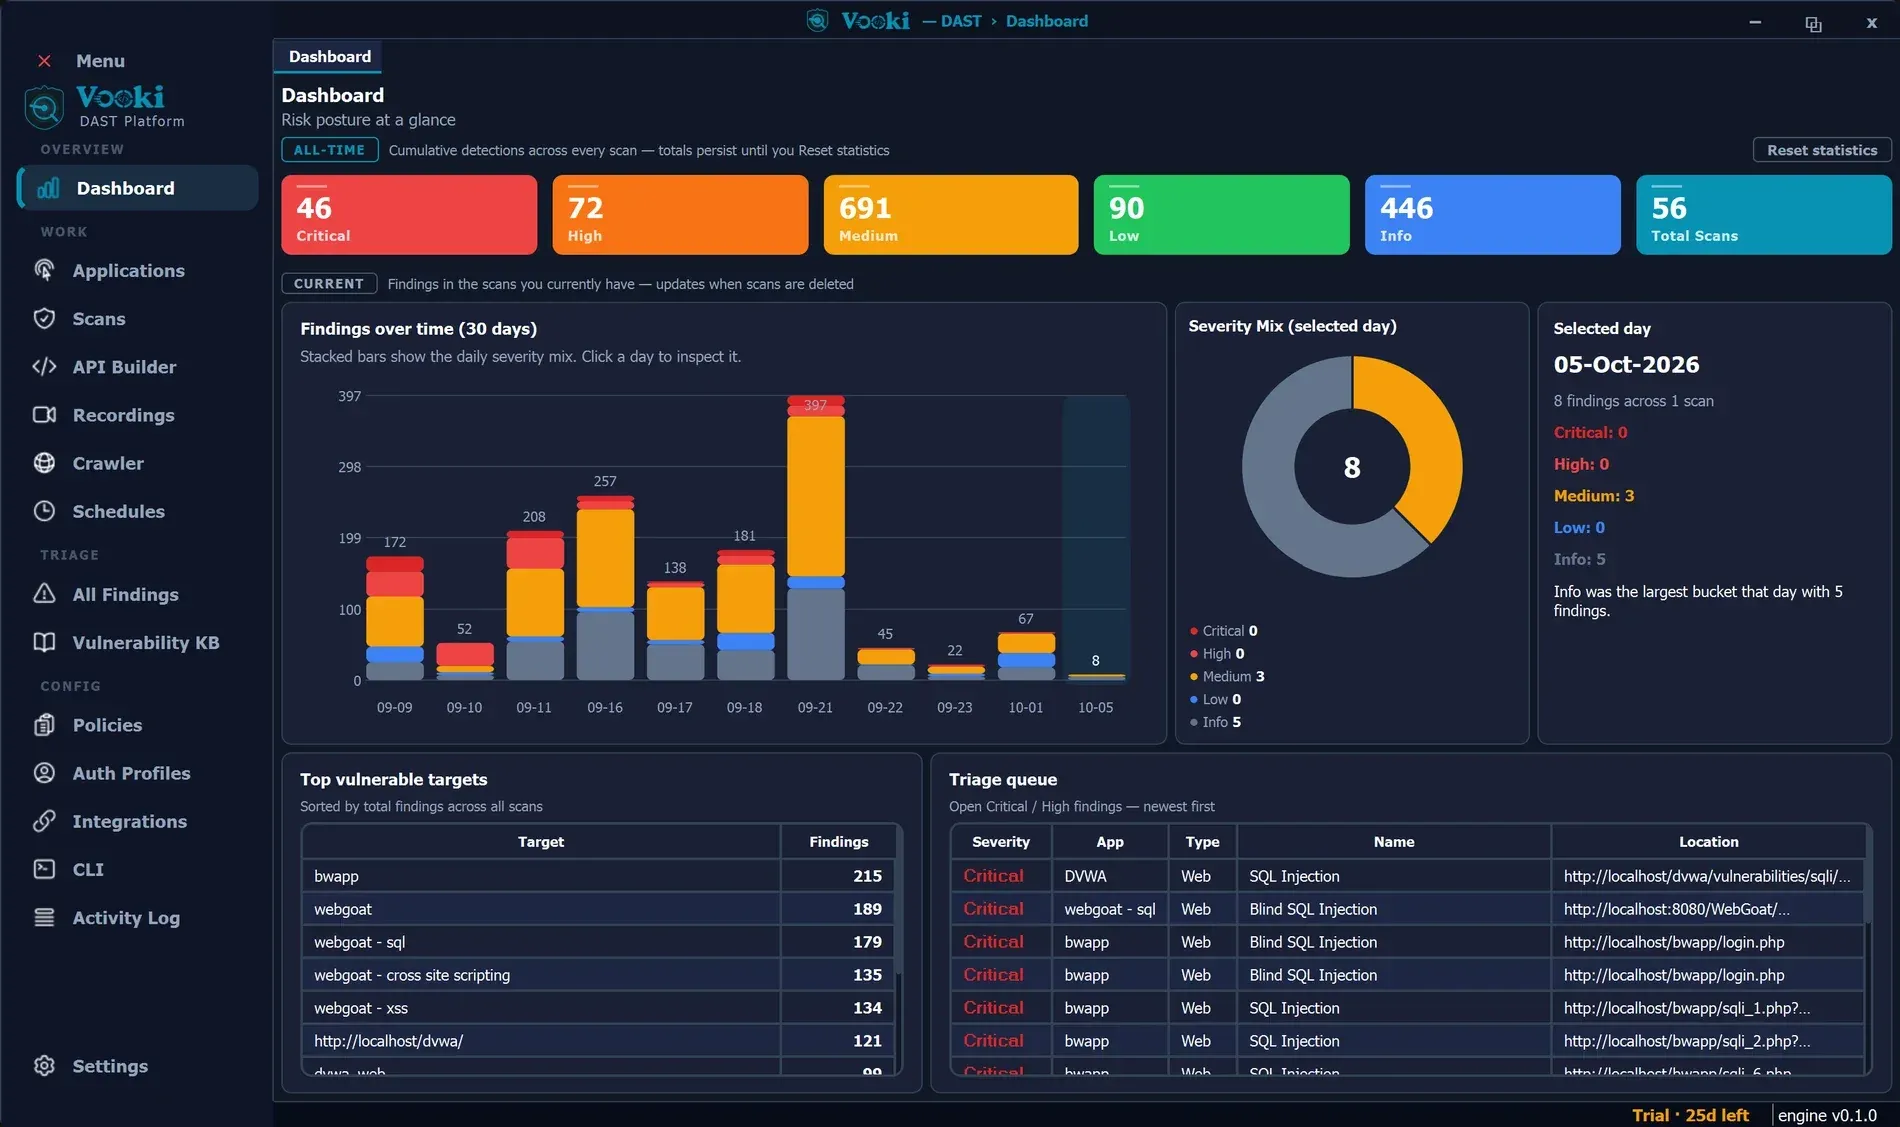
Vooki Pro DAST screenshots
Explore the interface. Open a screenshot to view it at full size.
Source: official Vooki Pro DAST project page.
Reviews of Vooki Pro DAST
No reviews yet
Be the first to share your experience with Vooki Pro DAST.
Write a review
Loading review form…
Alternatives to Vooki Pro DAST
 CapOpen-source, self-hosted CAPTCHA alternative using HashWX proof of work and instrumentation instead of image puzzles. Apache 2.0, Docker server with dashboard, a web component widget and a stateless core library.
 Contrast SecurityContrast Security uses in-app sensors for IAST, SAST and SCA, and its ADR and RASP layer detects and blocks attacks in production.
 DetectifyDetectify combines attack surface monitoring with DAST and API scanning, using findings from its ethical hacker community to prove what is exploitable.