

What is Saviynt?
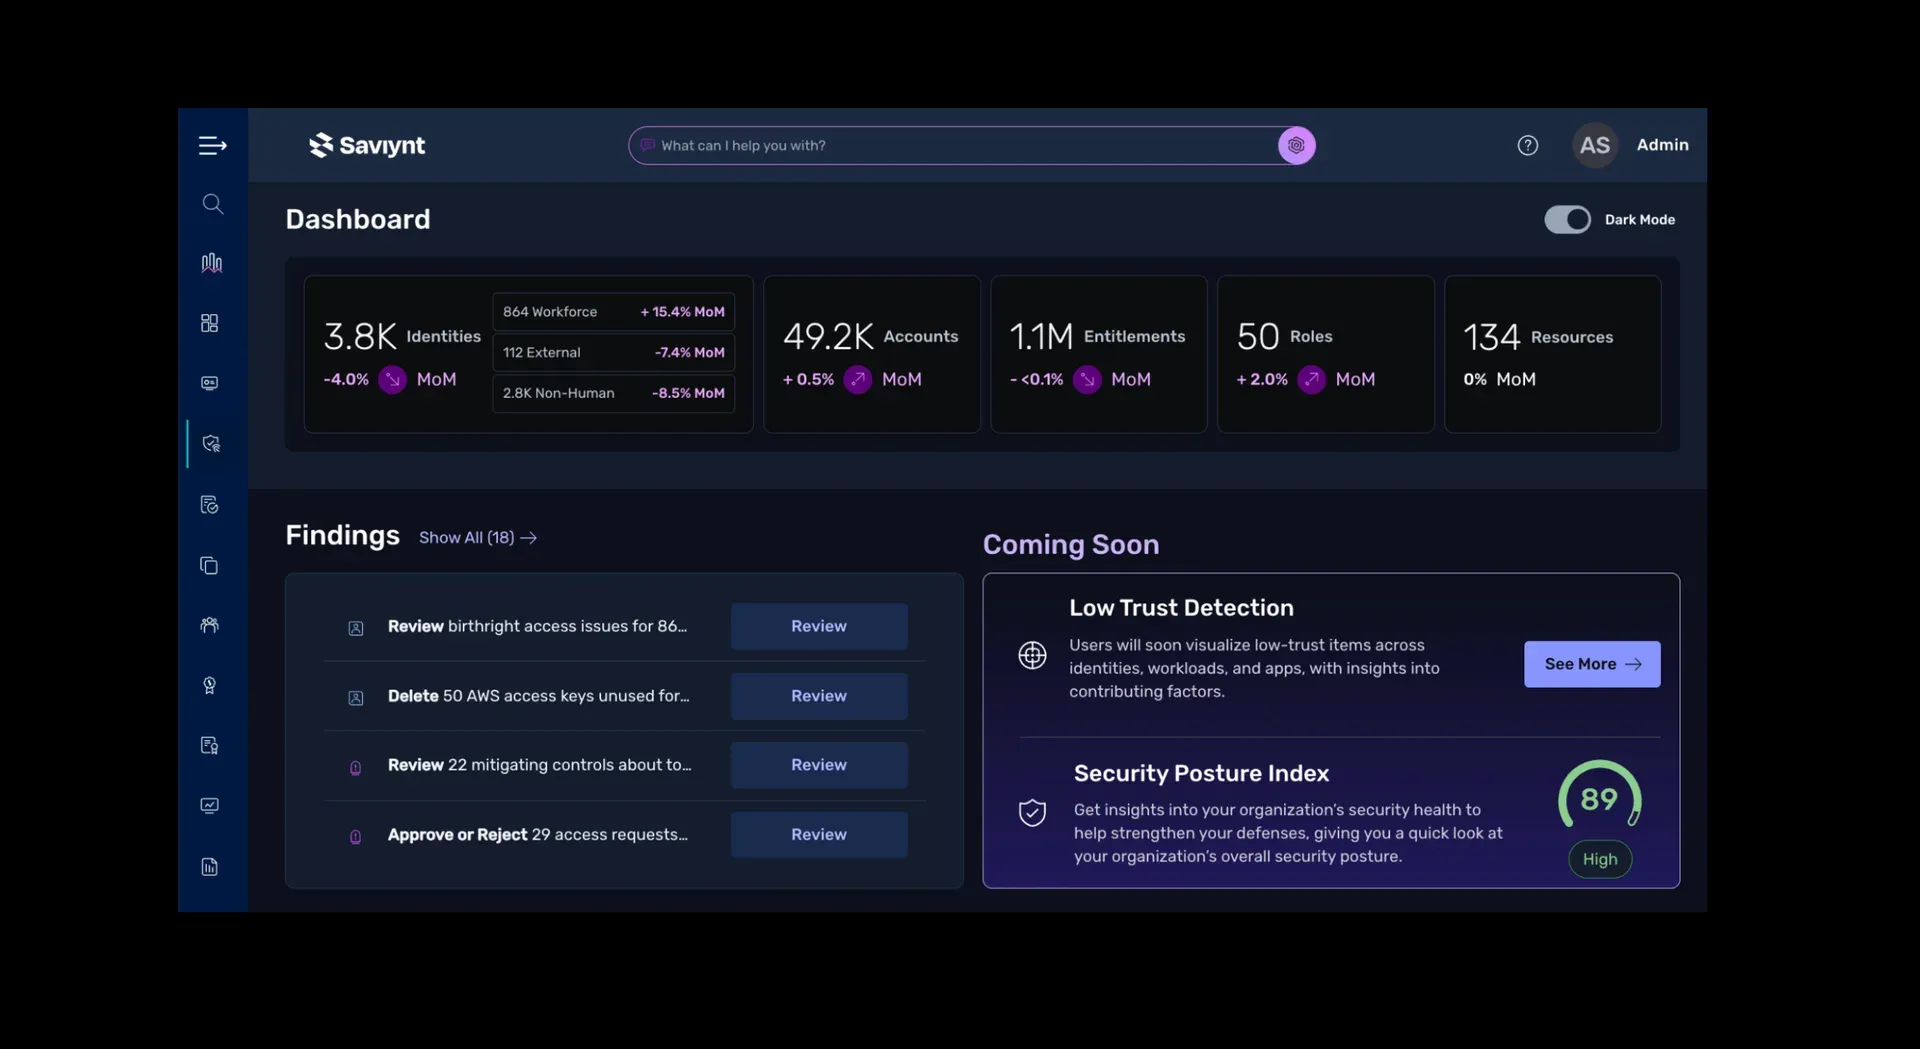
Saviynt is an identity security vendor whose Saviynt Identity Cloud combines identity governance and administration (IGA), privileged access management (PAM), application access governance, non-human identity management and identity security posture management on one platform. The about page describes the company's focus as cloud-first identity governance and access management and states that more than 100 million identities are secured with its products.
The leadership page names Sachin Nayyar as founder, CEO and chairman of the board. The contact page lists headquarters at 1301 E. El Segundo Blvd in El Segundo, California, with further offices in Reston (US Federal), Atlanta, Toronto, London, Sydney and Bengaluru, and 24/7 phone support for existing cases through the support portal.
The platform is delivered as a cloud-native service. Its governance scope covers human workforce and external users, privileged users, non-human identities such as workloads, service accounts and credentials, and AI agents, across SaaS, IaaS, on-premises and hybrid applications including ERP, EMR, CRM and HR systems. Saviynt has also announced Zuma, an AI identity security platform for AI agents and non-human identities with Zuma Insights, Zuma Access and Zuma Governance modules; the Zuma page offers a free start and a free trial.
Pricing for the Identity Cloud products is not published; the site routes buyers to demos and sales. Saviynt also offers expert services, a customer support portal, Saviynt University for training and certification, and a community site with user groups. The Trust and Security Center describes a DevSecOps program with third-party penetration testing, publishes security bulletins and links to a trust portal with compliance documentation.
Other identity governance and privileged access products listed on iThub include SailPoint, Idira (formerly CyberArk) and BeyondTrust.
Key capabilities
- Identity governance and administration Saviynt IGA governs internal, external, human and non-human identities in one platform and automates the identity lifecycle from onboarding to revocation on departure. The IGA page lists a catalog of pre-built integrations for SaaS, hybrid, on-premises, IaaS, ERP/EMR, CRM and HR systems.
- Access requests and certifications Access requests and certification campaigns use AI-powered recommendations. Saviynt states that up to 75% of access review decisions can be automated and that decision times for requests and reviews drop by up to 70%, with approver attention focused on higher-risk items.
- Saviynt Intelligence The intelligence layer provides trust scoring that combines multiple risk indicators and peer access analytics into one weighted score, with adjustable signal weights and thresholds. It also covers intelligent access recommendations, duplicate identity management and access modeling, as described on the intelligence page.
- Privileged access management Saviynt PAM covers discovery of privileged access, vaulting, session recording and remote privileged access from one control panel, aimed at zero standing privilege for human, non-human and AI identities. An Agent Access Gateway and privileged access governance are part of the module, per the PAM page.
- Just-in-Time Access Just-in-Time Access replaces standing access to high-risk entitlements with time-bound, policy-driven access granted through an automated request-to-approval workflow. It discovers users and shared accounts holding high-risk entitlements in cloud and on-premises apps, and Saviynt states it can be activated for all connected apps within an hour.
- Application Access Governance AAG provides fine-grained visibility into access and entitlements in applications such as SAP, Oracle and Workday, out-of-the-box segregation of duties (SoD) rulesets, AI-powered risk analytics, automated certifications, emergency access management and license cost optimization. It monitors access across more than 100 cloud and on-premises applications.
- Identity security for SAP A dedicated SAP offering covers identity, application and privileged access governance for SAP and hybrid SAP landscapes, including cross-application SoD detection and emergency access management.
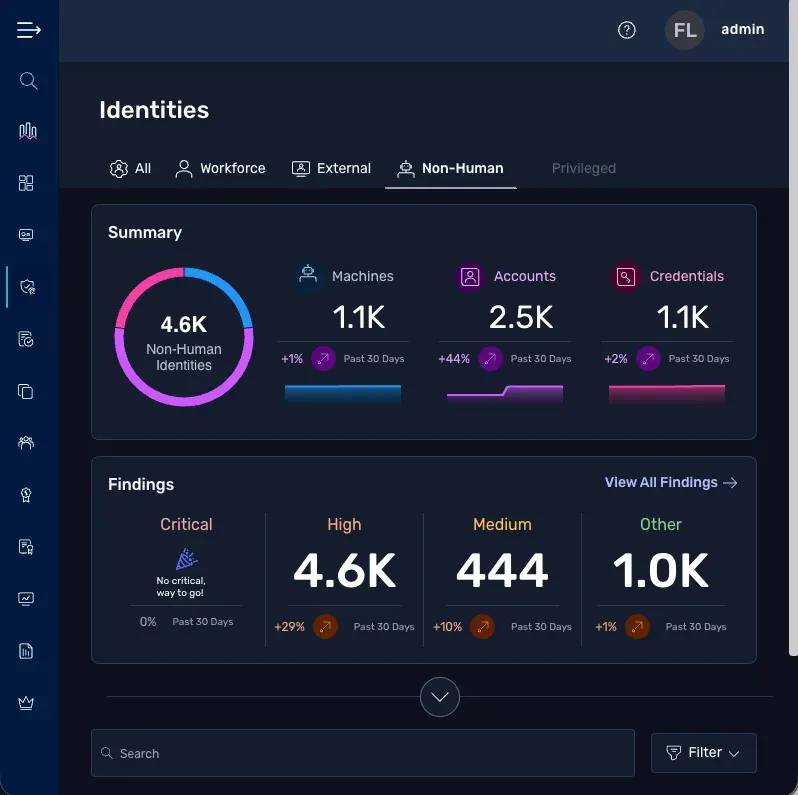
- Non-human identity management The NHI module discovers workloads, accounts and credentials across apps and environments, builds a real-time inventory, evaluates risk from critical to low with context, maps access relationships and keeps a timeline of lifecycle changes. Remediation includes one-click ticket creation and AI-guided recommendations.
- Identity Security Posture Management ISPM discovers identities, access and assets, correlates them to detect risky access, prioritizes remediation and improves identity data hygiene. A timeline view records every attribute change and access assignment for audit preparation, according to the ISPM page.
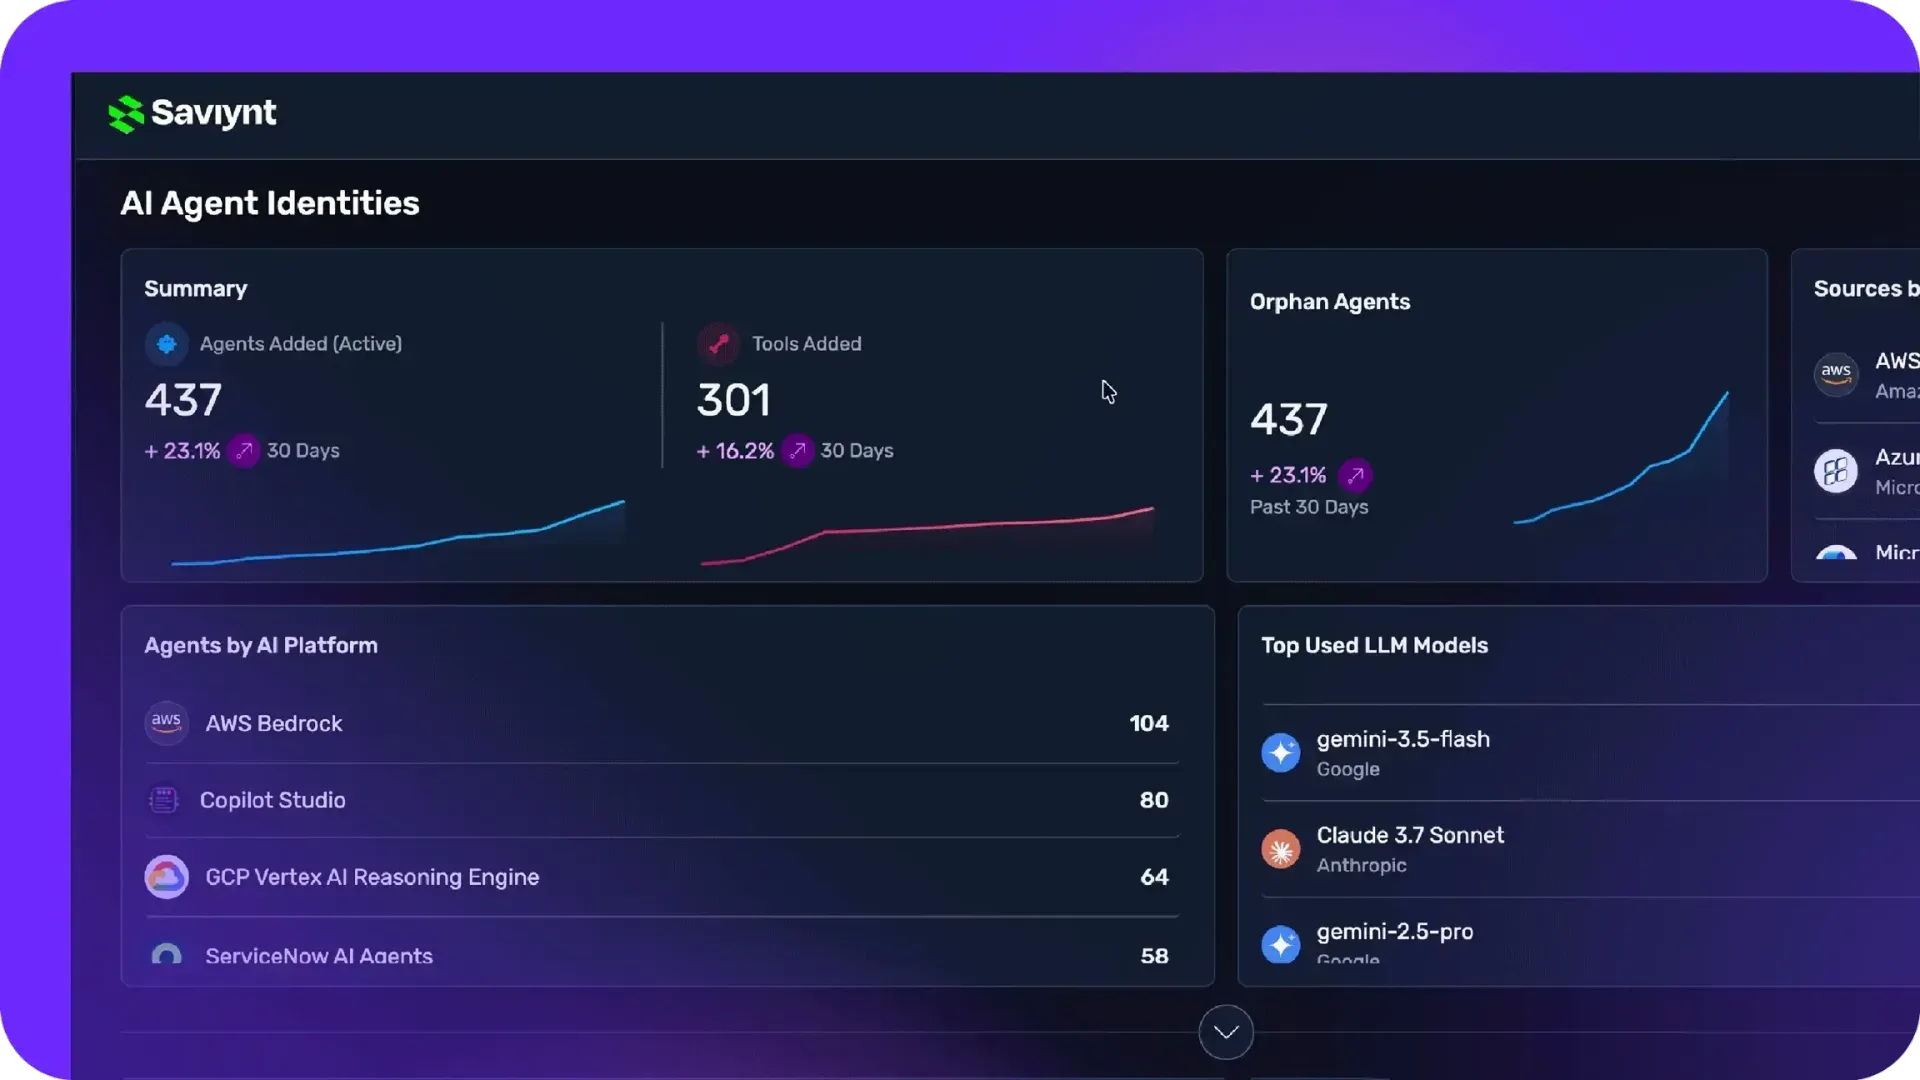
- Zuma Insights Zuma automatically discovers AI agents, tools, MCP servers and NHIs, prioritizes risks by business impact, maps the access path an agent takes to apps and data, and keeps a timeline of agent actions and changes.
- Zuma Access Zuma Access authenticates whether an agent acts on its own or on behalf of a user, enforces intent-aware runtime authorization based on identity, context and risk, and applies fine-grained policies on what agents may do inside applications. Zuma for Apps extends this to allowing, blocking or escalating agent actions in business applications.
- Zuma Governance Agents are registered in a few clicks or through an API, assigned owners with succession management, governed through request and approval workflows for human-to-agent and agent-to-resource access, and removed with a kill switch for orphaned or unmanaged agents.
- Saviynt MCP Server The Model Context Protocol server lets authorized AI agents and users query identity data in natural language, such as who has access to what, and trigger governance workflows like access reviews, certifications and revocations. It is listed in the AWS Marketplace AI Agents and Tools category, per the MCP Server page.
- Integrations Integration pages on the Saviynt site cover partners and platforms such as Amazon Web Services, CrowdStrike, ServiceNow, Wiz and Zscaler, in addition to the connector catalog for governed applications.
- Security and trust The Trust and Security Center describes regular third-party penetration testing, internal use of Saviynt's own platform for security management, the option to mask a customer instance from the internet during elevated threat levels, encrypted communication to managed endpoints and public security bulletins. Saviynt has signed the CISA pledge.
- Support and training Customers open cases through the support portal and can use an automated 24/7 phone line to take critical action on existing cases. Saviynt University offers free trainings, certifications and courses, and expert services support implementations.
Where Saviynt fits
Joiner, mover and leaver automation
Organisations integrate HR systems so that Saviynt provisions birthright access when an employee joins, adjusts it on role changes and revokes it automatically on departure. External users such as contractors and suppliers are governed in the same platform.
Periodic access certifications for audit
Compliance teams run certification campaigns where managers and application owners review access, with AI recommendations pre-scoring low-risk items. Audit evidence and timelines of identity changes support internal and external audits, as described on the intelligence page.
Segregation of duties in ERP systems
Finance and GRC teams use Application Access Governance with out-of-the-box SoD rulesets to detect conflicting entitlements in SAP, Oracle or Workday, mitigate violations and manage emergency access, with license cost optimization for the governed applications.
Reducing standing privileges
Security teams discover privileged and high-risk access across cloud, SaaS, DevOps and infrastructure, then move users to Just-in-Time Access with time-bound approvals, vaulting and session recording through the JIT and PAM modules.
Governing machine and AI identities
Teams inventory service accounts, workloads, credentials and AI agents, assign owners, review risky access and offboard orphaned identities. Zuma adds discovery of shadow AI, runtime authorization of agent actions and an agent registry. Through the Saviynt MCP Server, authorized users and agents can also ask questions such as who has access to what and trigger reviews, certifications or revocations in natural language.
Modernizing a legacy IGA deployment
Saviynt lists legacy IGA modernization, mergers and divestitures, multicloud security and zero trust among its use-case pages, each describing how the Identity Cloud platform is applied to that scenario. Customers onboard applications once and enable additional features later.
Reviews of Saviynt
Be the first to share your experience with Saviynt.
Write a review
Loading review form…
Found Saviynt useful? Upvote it todayYour vote helps other IT teams find it in the daily ranking.


