What is IntuneGet?
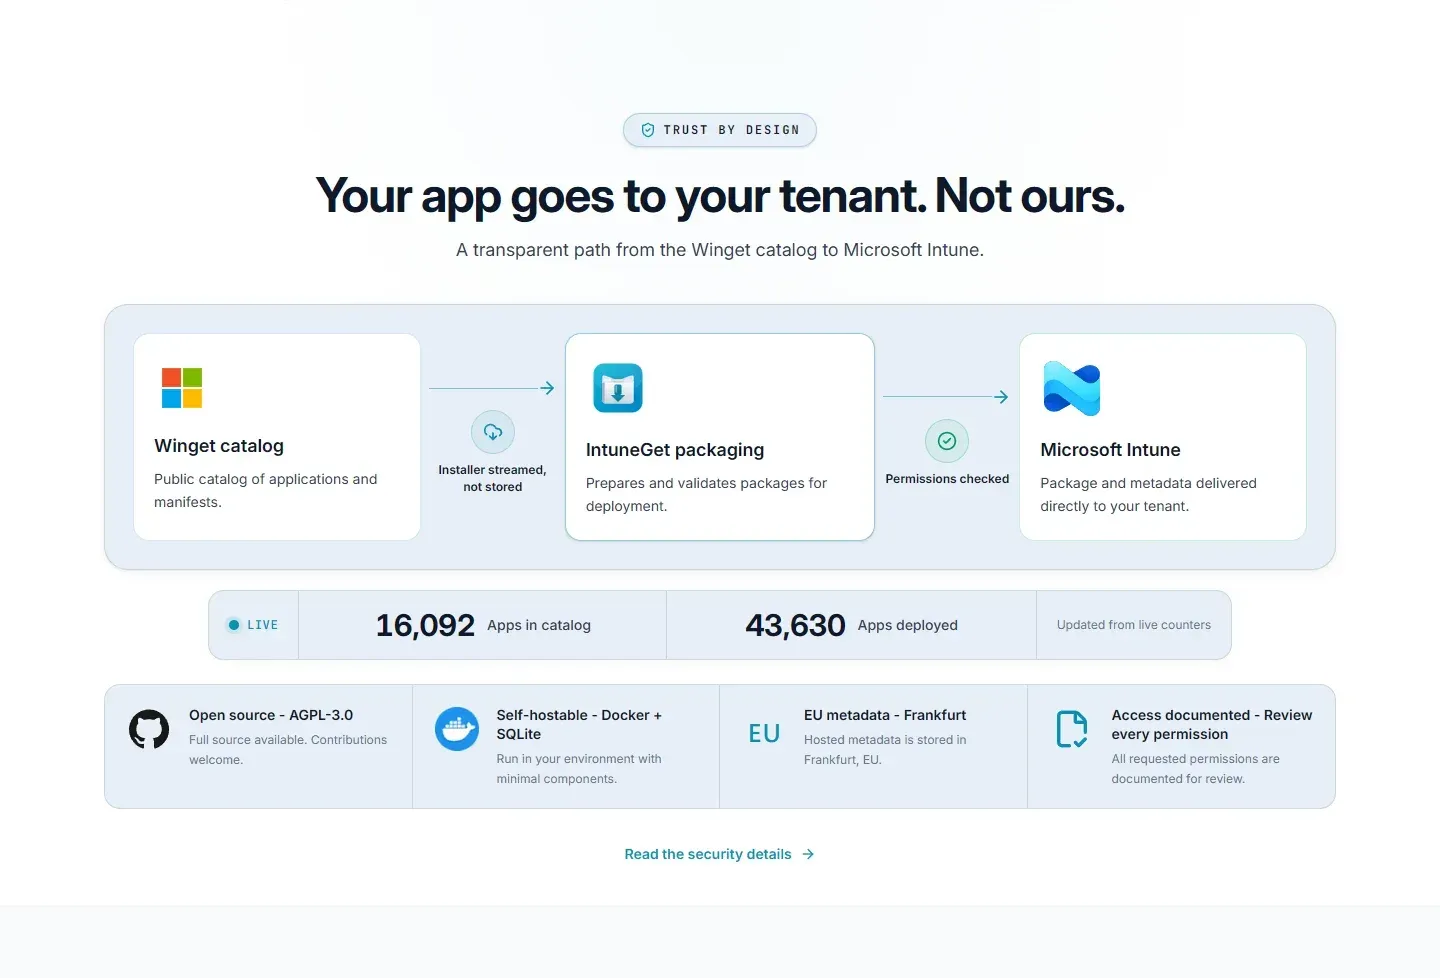
IntuneGet is an open-source web application that turns entries from the public Winget catalog into Win32 apps in a Microsoft Intune tenant. An administrator searches the catalog, reviews the version, architecture, install behavior and assignments, and IntuneGet packages the installer as an .intunewin file, generates detection rules and uploads the result through the Microsoft Graph API. The project is published by Ugur Koc under the UgurLabs name; its website describes it as a personal project that began as a script for repetitive Intune packaging work. The code is on GitHub and the product site is intuneget.com.
There are two ways to run it. The hosted service at intuneget.com is free to use and stores operational metadata (account email, deployment history, app catalog and team settings) in the EU, in the Supabase Frankfurt region, according to the security page. The same code can be self-hosted with Docker Compose or on Vercel, using Supabase Cloud, a self-hosted Supabase stack or an embedded SQLite file. Packaging runs either on GitHub Actions Windows runners or on a local Windows packager, which is distributed as the npm package @ugurkocde/intuneget-packager and requires Node.js 22 or later on Windows 10/11 or Windows Server 2019 and later.
The latest GitHub release is the packager-v1.4.3 npm packager, published on November 3, 2026. The web application and its Docker image are versioned separately: v0.8.5, published on October 29, 2026, fixes automatic-update history in self-hosted SQLite installations so that finished local packaging jobs are recorded as Completed, Failed or Cancelled and repeated completion reports do not count a failure twice. The 0.8 series is pre-1.0, so expect interface and schema changes between releases.
The application is built with Next.js 14, React and TypeScript, with shadcn/ui and Tailwind CSS for the interface, Zustand and TanStack Query for state, MSAL for Microsoft Entra ID sign-in and Supabase (PostgreSQL) or SQLite for storage. The source is licensed under the GNU Affero General Public License v3.0, which requires that modified versions offered as a network service publish their source. IntuneGet is not an endpoint manager: it does not replace Intune, enroll devices or run a client agent. It prepares and uploads packages, and the installation on devices stays with Intune. The website states that IntuneGet is not SOC 2 certified, so review the documentation against your own compliance requirements.
Key capabilities
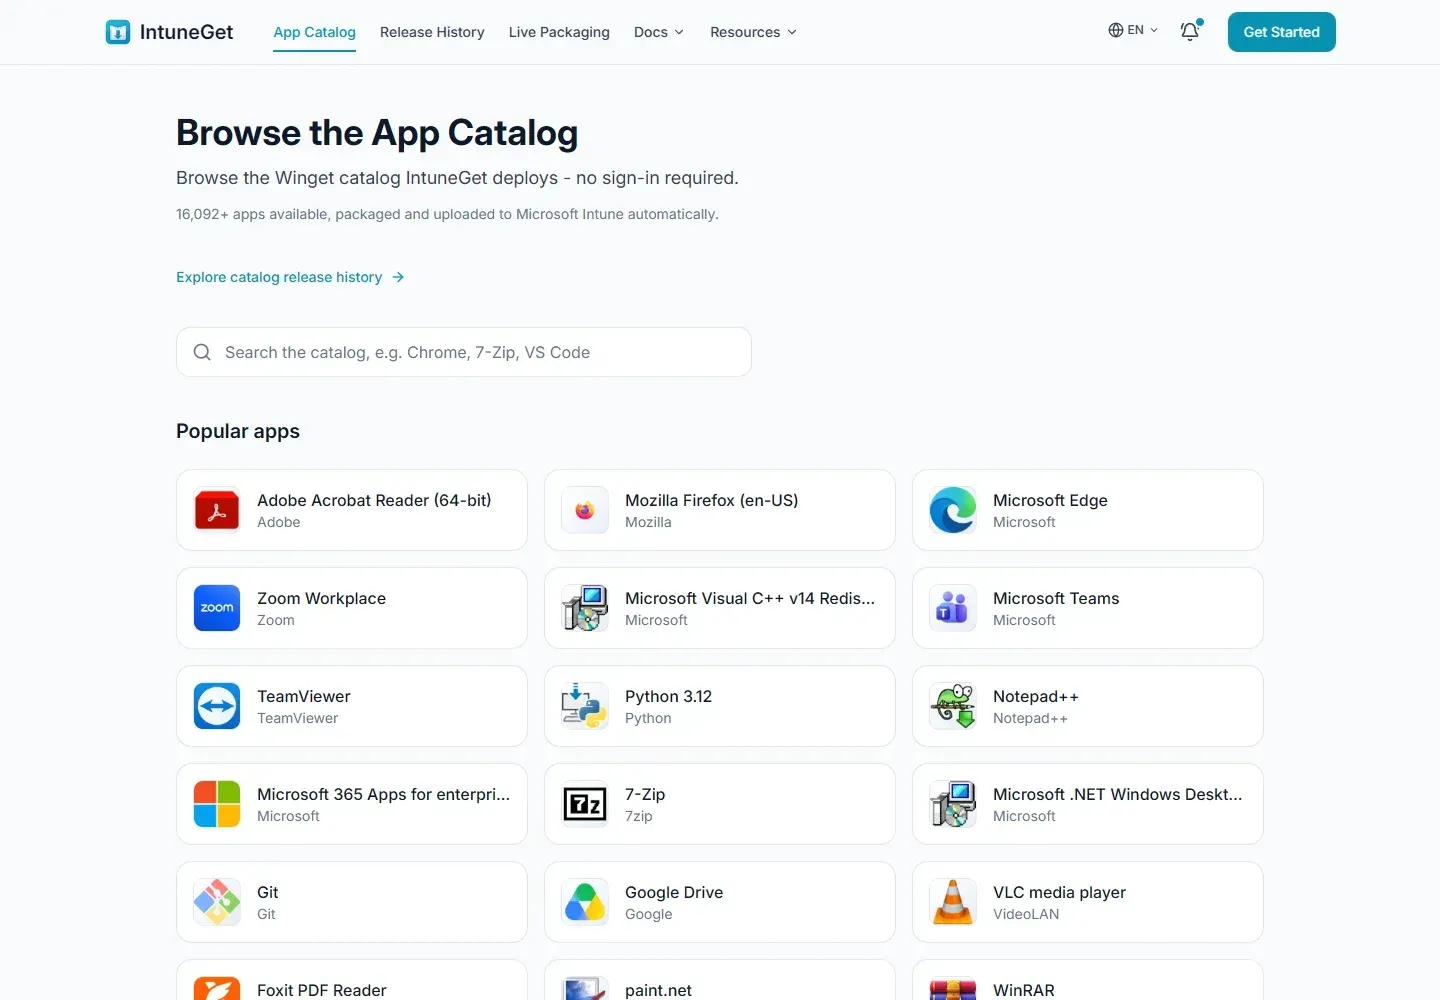
- Winget app catalog Search the public Winget catalog without signing in. The product site reports a catalog of more than 16,000 apps, and each one is addressed by its exact catalog ID (for example
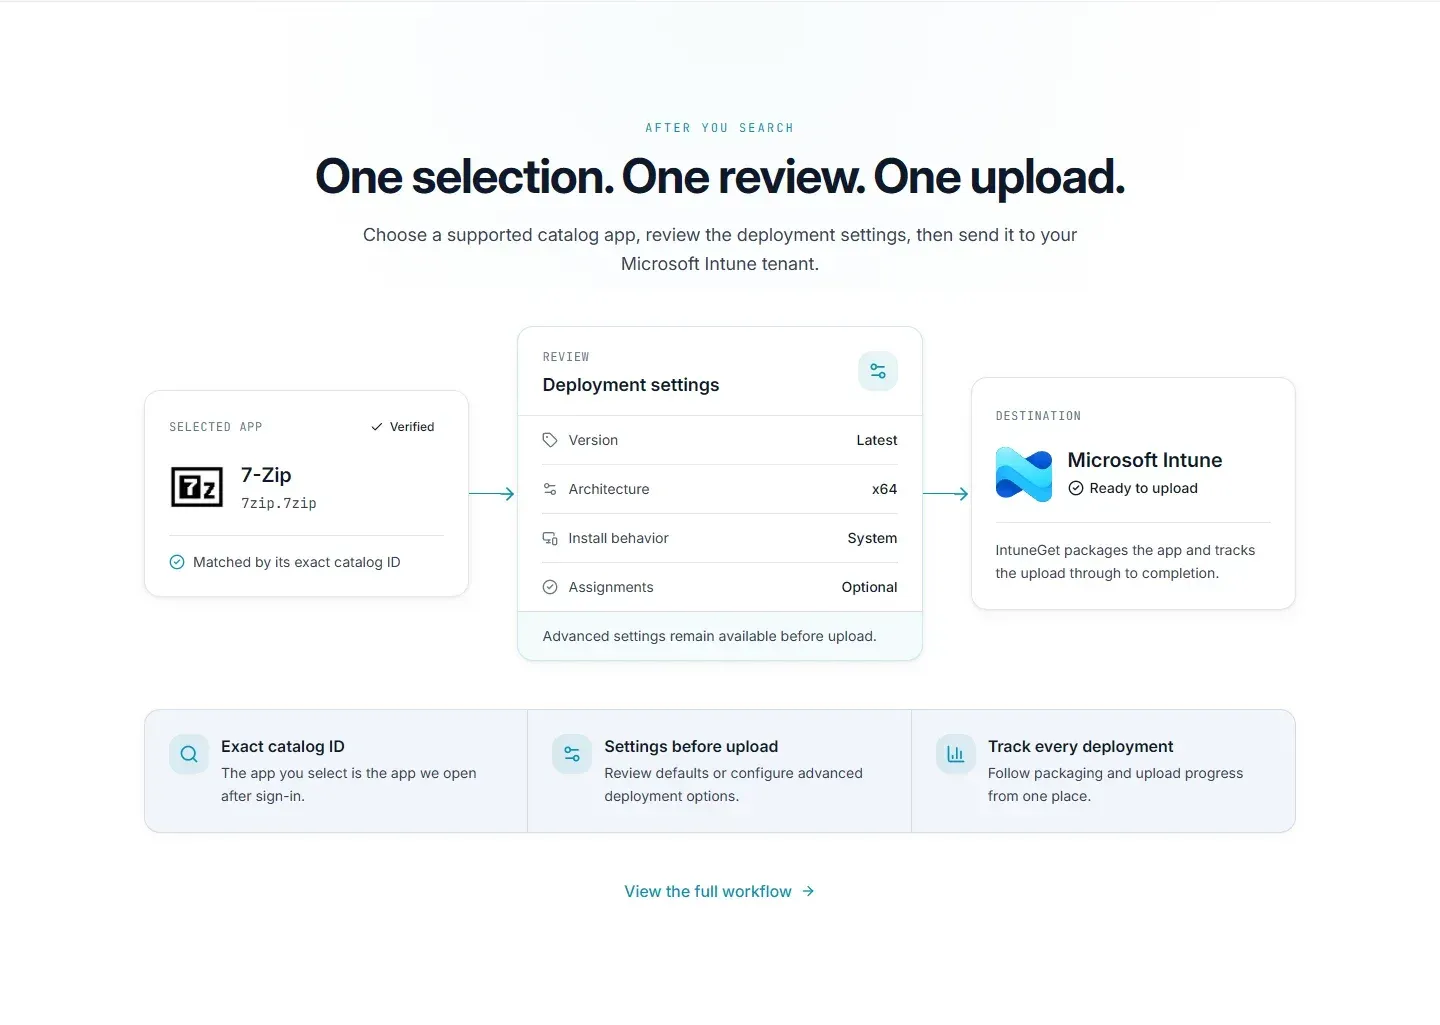
7zip.7zip), so the app you select is the app opened after sign-in. The catalog is browsable on the app catalog page. - One-click deployment to Intune Choose an app, review version, architecture, install behavior (system or user) and optional assignments, then send it to the tenant. IntuneGet downloads the installer, builds the
.intunewinpackage and uploads it through Microsoft Graph. Advanced settings stay available before upload. - Generated detection rules and silent switches Detection rules and silent install parameters come from Winget manifest data rather than hand-written scripts. This removes the most error-prone part of manual Win32 packaging, but an unusual installer can still need a custom command line, so check the generated values for apps you rely on.
- PSADT v4 packaging Apps can be wrapped with the PowerShell App Deployment Toolkit v4 to add dialogs, balloon tips and process handling. The repository publishes a PSADT coverage document listing which options are generated and tested.
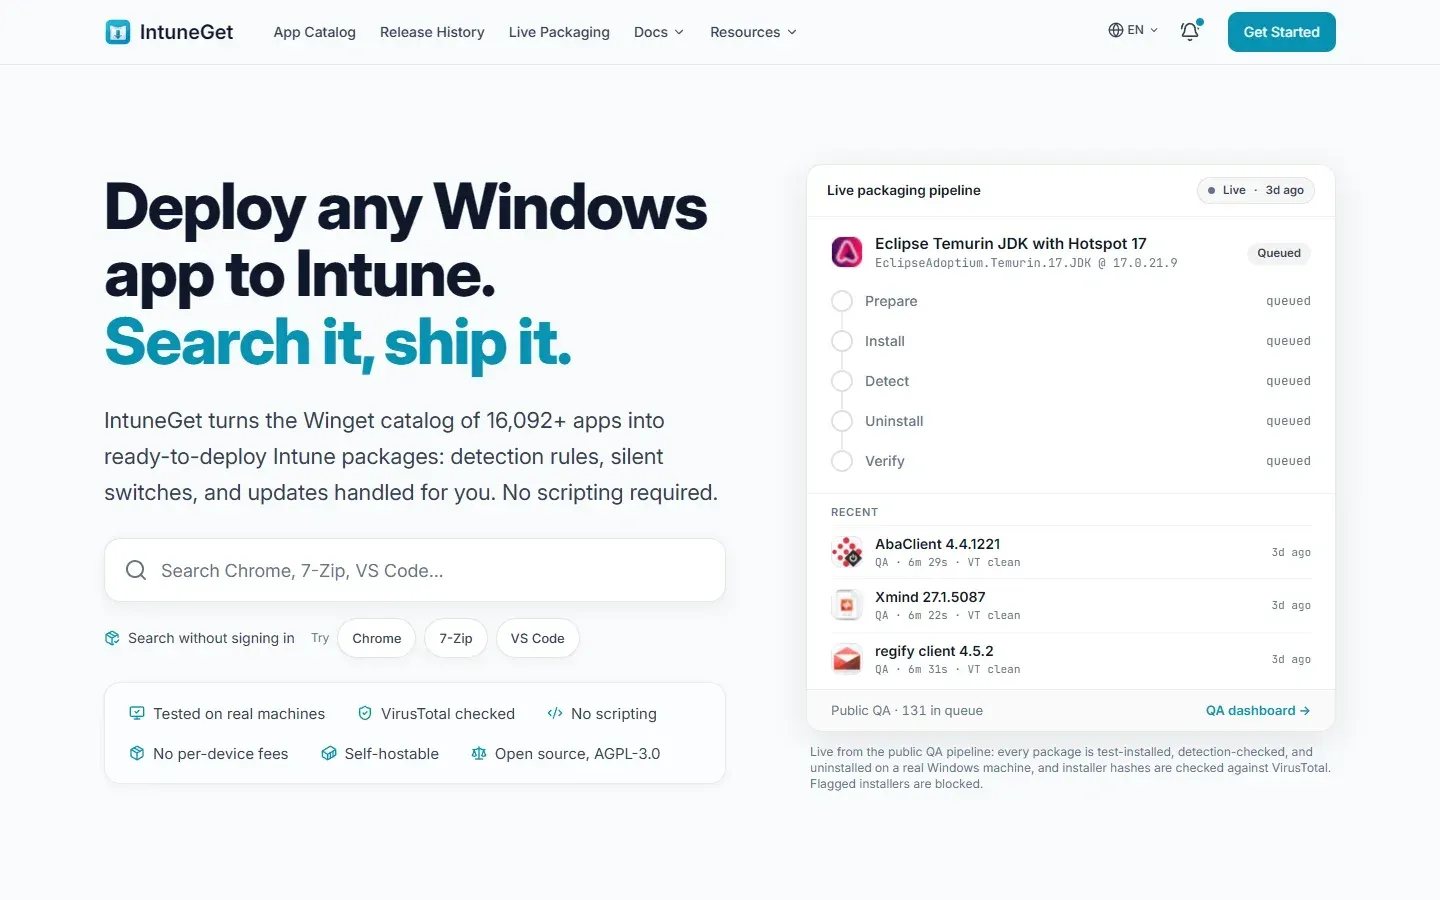
- Live packaging pipeline and public QA The site shows a live pipeline in which packages are test-installed, detection-checked and uninstalled on a real Windows machine, with installer hashes checked against VirusTotal. The site states that flagged installers are blocked. These are project claims about its own QA pipeline.
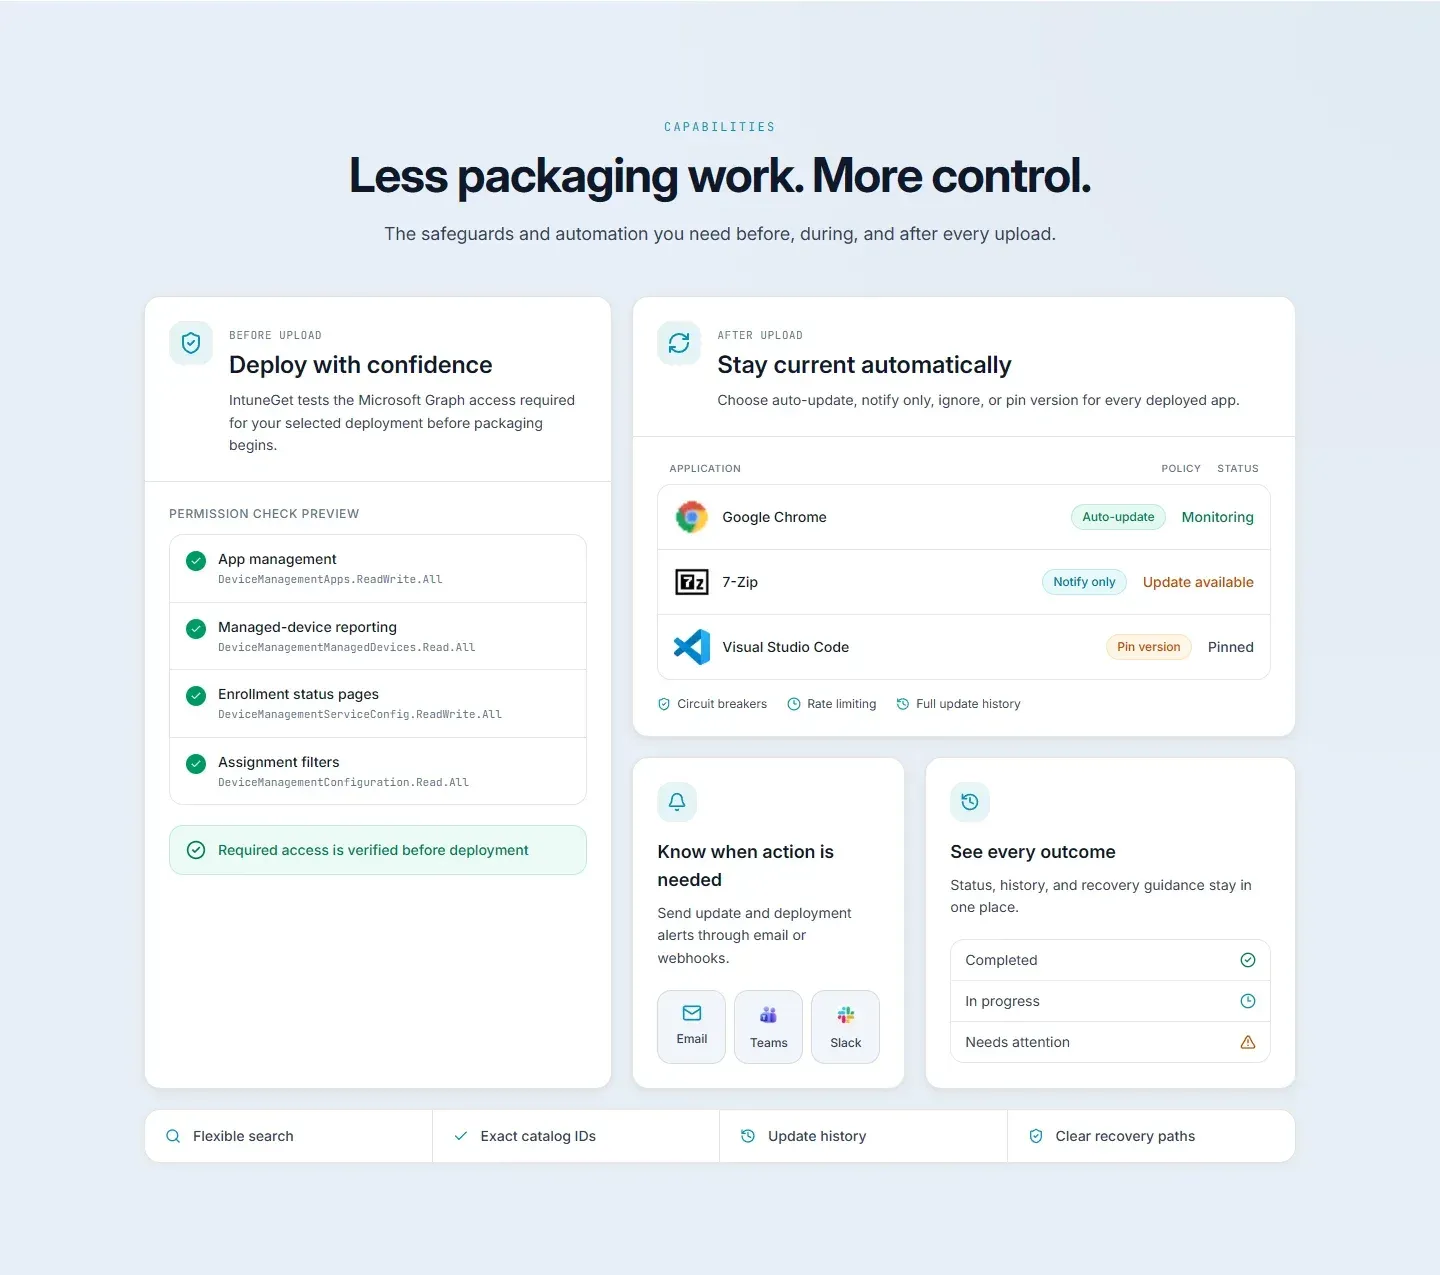
- Pre-upload permission check IntuneGet tests the Microsoft Graph access needed for the selected deployment before packaging begins, so a missing admin consent shows up early. Required permissions are a single delegated scope,
User.Read, plus five application permissions:DeviceManagementApps.ReadWrite.All,DeviceManagementServiceConfig.ReadWrite.All,DeviceManagementConfiguration.Read.All,DeviceManagementManagedDevices.Read.AllandGroupMember.Read.All. - Automatic updates and update policies Each deployed app can follow a policy: auto-update, notify only, ignore, or pin to a version. Auto-update scope can be limited to all updates, minor and major, or major only; the documentation warns that major-only can delay security fixes shipped in minor releases. Safeguards include a consecutive-failure threshold, hourly caps, cooldown windows and consent verification, and a manual trigger accepts at most 10 items per request.
- Custom apps An installer that is not in Winget can be packaged from a URL by entering publisher, name, version, installer type and architecture. Generic EXE installers need the vendor documented silent switches. Saved definitions keep reusable metadata but not installer URLs or hashes, and direct file upload is not part of the feature. See the custom apps guide.
- Curated catalog pilot A separate IntuneGet-owned catalog uses
IntuneGet.Curated.*identifiers and publisher-sourced installers, for example Chrome, Firefox ESR, 7-Zip, Visual Studio Code, Git and Wireshark, with SHA256 values pinned where the publisher provides them. It does not resolve packages through Winget. The curated catalog document describes the trust model. - SCCM migration Import an SCCM application export (CSV or JSON, produced with the supplied
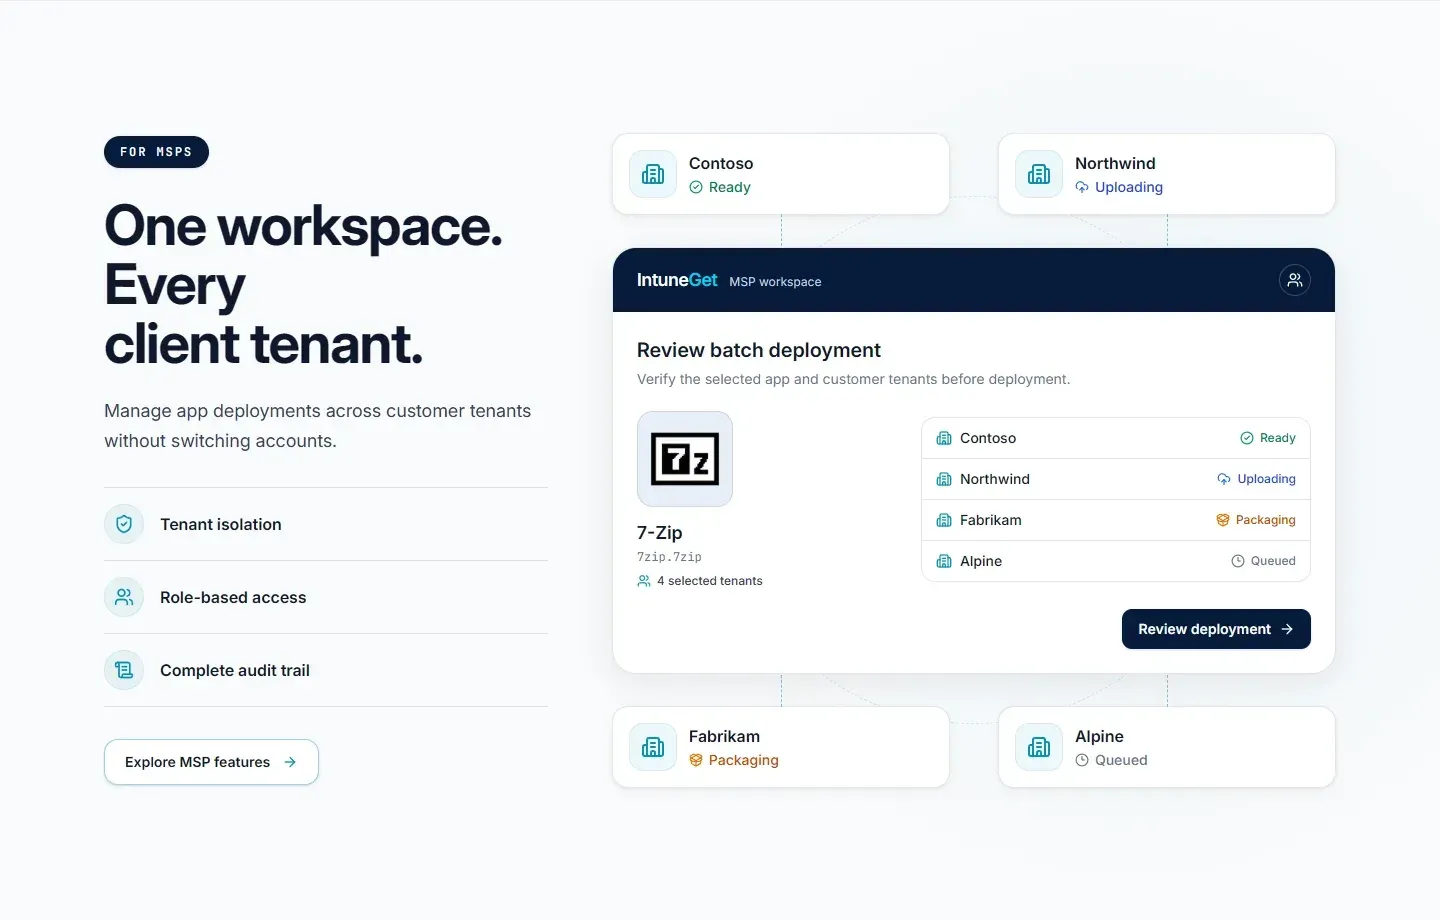
Export-SCCMApps.ps1script), run automatic and manual matching against Winget packages, preview blockers and queue the selected apps into the packaging pipeline. Script detection conversion mainly supports PowerShell, and some technologies such as App-V are marked unsupported. - MSP mode and multi-tenant batches Managed service providers can work with several customer tenants from one workspace, keep tenant data separated and deploy one app to several tenants at once with configurable concurrency. Teams use Owner, Admin, Operator and Viewer roles, and a log viewer records IP address, user agent and time for MSP operations.
- Inventory, reports and uploads Dashboards list the Intune Win32 apps in the tenant with assignments, show success rates, daily trends, top apps and recent failures, and export reports to CSV, JSON or PDF. The uploads page tracks packaging and deployment jobs with cancel, dismiss and force-redeploy actions.
- Notifications and webhooks Deployment and update events can be sent in the app, by email, or to Slack, Teams, Discord or custom webhook endpoints with delivery logging and retry. Configure webhooks from the settings pages described in the documentation.
- Community ratings and suggestions Admins can rate apps, suggest new catalog entries and vote on suggestions. Community endpoints use in-memory rate limits of 30 requests per minute for public reads and 10 per minute for authenticated writes, per the API reference.
- Self-hosting with Docker Compose Clone the repository, copy
.env.exampleto.env.local, set the Microsoft Entra ID client values andDATABASE_MODE, then rundocker-compose up -d; the app listens on port 3000. With SQLite, the database lives at/data/intuneget.dbin a named volume, which must be backed up. The self-hosting guide lists all variables. - Local Windows packager For air-gapped or fully self-managed setups, run the npm packager on Windows instead of GitHub Actions. It polls for jobs, downloads installers, builds PSADT packages, converts them with
IntuneWinAppUtil.exeand uploads to Intune, and it offerscheck,setupand--dry-runcommands. Releases are published as provenance-attested npm packages. - Server diagnostics for operators Self-hosted servers accept
INTUNEGET_LOG_LEVEL(debug, info, warn, error) and an optional log directory with 5 MiB rotation and three backups. File logs redact credential patterns, URLs, email addresses and UUIDs, but the documentation still advises treating logs as sensitive. - REST API The application exposes endpoints for packaging jobs, updates and policies, SCCM migrations, inventory and analytics. Most require a Microsoft access token as a bearer token, and pipeline callbacks use HMAC signatures. The API reference groups them by feature.
Where IntuneGet fits
Packaging a standard application set
Search for the applications you deploy most, confirm the architecture and install scope (system for most corporate apps), and review the detection rule before upload. Assign to a pilot group first, then widen. Check the Intune app list afterwards: the app should appear as a Win32 app with the generated install and uninstall commands. The documentation walks through the first deployment.
Keeping deployed apps current
Open the Updates page, pick a policy per app and choose the version scope. Use notify only for apps where a version change needs a test, auto-update for low-risk tools and pin version for software with strict compatibility. Review the auto-update history for failures, because policies that pass the failure threshold can be disabled automatically. The updates and policy guide lists the endpoints and limits.
Managing several customer tenants as an MSP
Enable MSP mode, add each customer tenant, have that tenant Global Administrator grant admin consent and assign team roles. A batch deployment pushes one app to the selected tenants with a chosen concurrency. Verify tenant isolation and the audit log before onboarding production customers. The documentation has an MSP features page.
Migrating applications away from SCCM
Run the supplied export script on the SCCM side, import the CSV or JSON file, and run matching. Resolve partial and unmatched rows manually or exclude them, then read the preview for blockers such as missing installer metadata or unsupported detection rules. Execute the migration only for rows without blockers. The SCCM migration guide lists current limits, including synchronous matching on large imports.
Self-hosting in a controlled environment
Register a multi-tenant Entra ID application, grant the five application permissions, choose SQLite or Supabase and select GitHub Actions or the local packager. Keep the client secret and the packager API key in a secret store, back up the data volume and restrict access to logs. The Entra ID setup guide recommends a 24 month secret lifetime, so put the expiry in a calendar.
Packaging software that Winget does not carry
Use Add Custom App with a direct installer URL, supply the vendor silent switches and a trusted SHA256 when available, and save the definition for later versions. For private storage, use a read-only signed URL that stays valid until packaging finishes. See the custom apps document for what is and is not stored.
Reviews of IntuneGet
Be the first to share your experience with IntuneGet.
Write a review
Loading review form…
Found IntuneGet useful? Upvote it todayYour vote helps other IT teams find it in the daily ranking.